Your Security Stack Under One Integrated View

Peer Review

Gartner brand name text logo in white with registered trademark symbol.
5-star rating
4.8

Proven Trust

Dark blue circle with two overlapping checkmarks, one green and one light blue.
ISO 27001 text with a globe outline symbol on a black background.
2025 winner badge for Cyber Security Excellence Awards with gold and black design.

Keep the tools you've already invested in. VisionX runs on top of your SIEM, EDR, and XDR platforms and brings what they find into one view, with the context your team needs to act.

Talk to our team
SentinelOne company logo with stylized shield icon to the left of the text.

319% ROI

Independent ROI Study

<6 Months

Payback

€2M

Net Present Value
By now, most organisations have already
suffered significant business impact.
HOW PHISHING REPORTING WORKS

From One Click to a Resolved Case

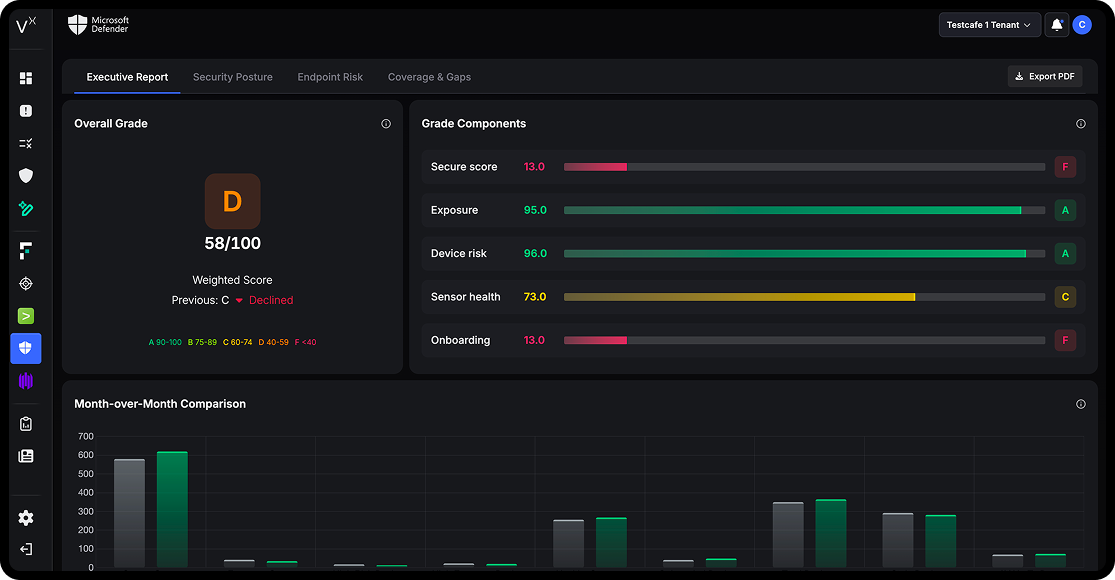
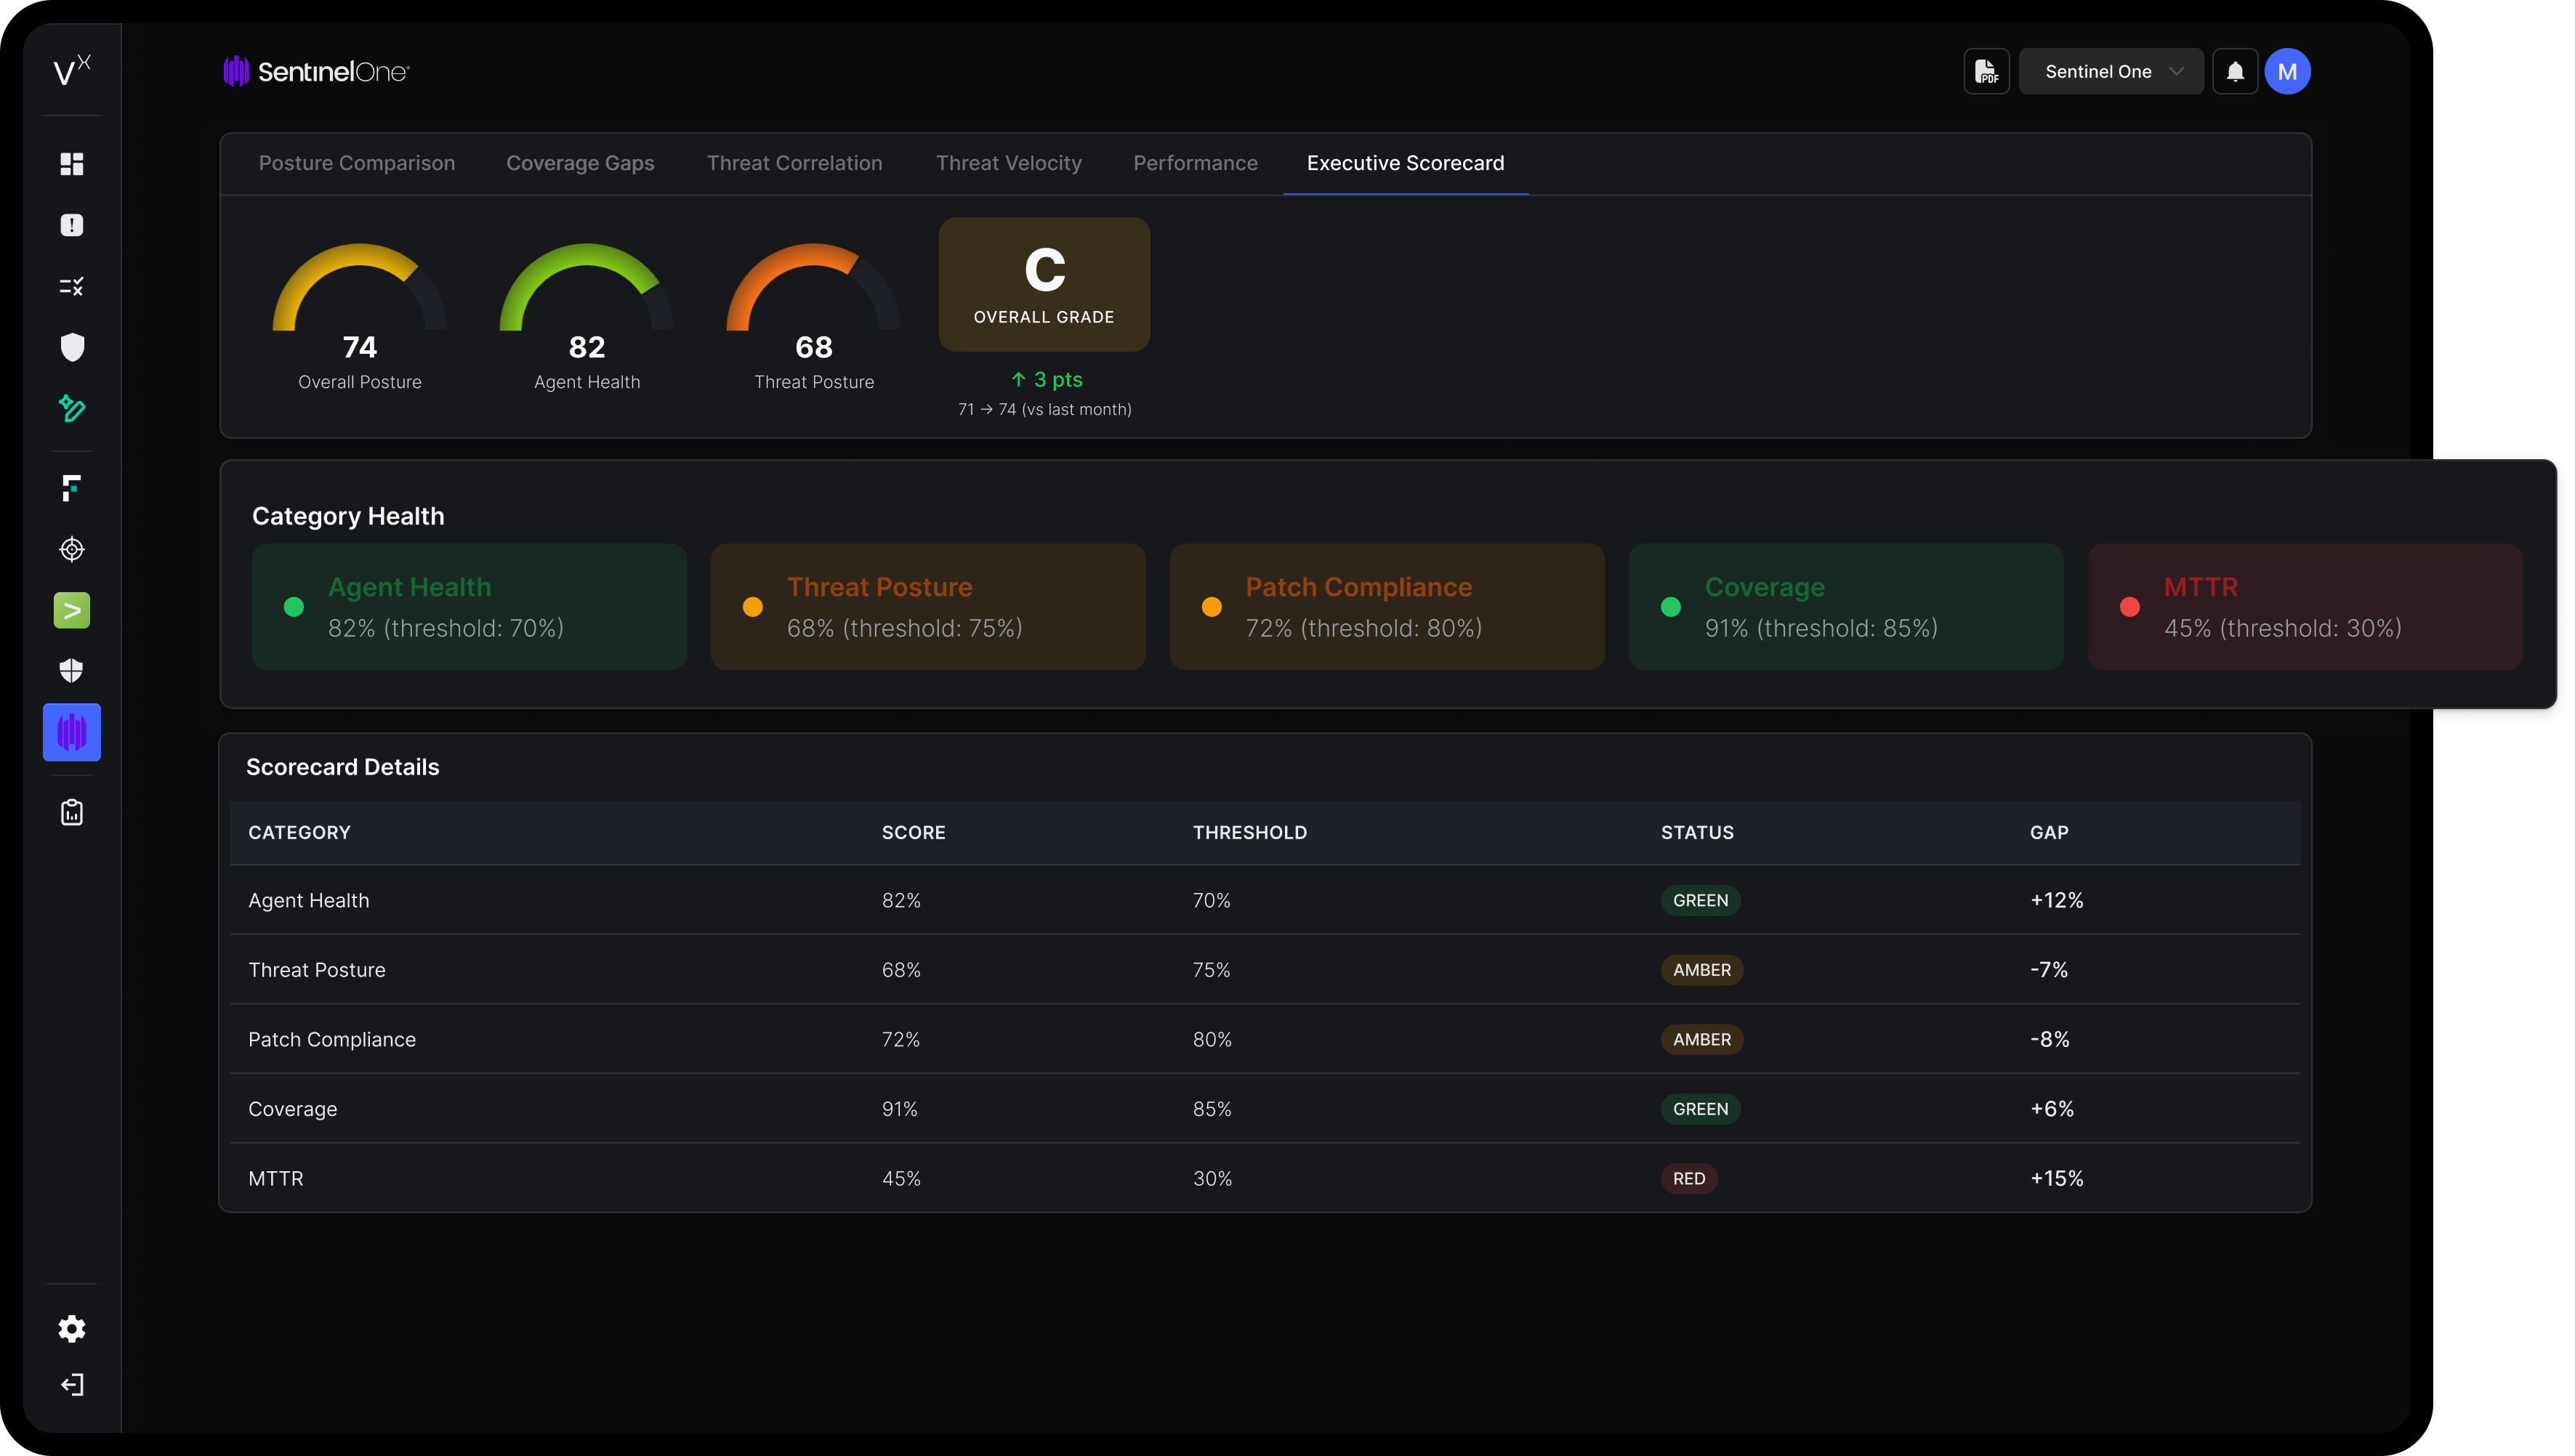
Turn Defender's signals into a board-readable endpoint report

A weighted score out of 100 with its trend against the previous period, plus grades for secure score, exposure, device risk, sensor health, and onboarding. Month-over-month comparison and a metrics scorecard show what moved, and the report exports to PDF.
User Views
Executive Report
Security Posture
Endpoint Risk
Coverage and Gaps

See what your automation delivers and which users carry the most risk

An automation summary covering resolved events, mean dwell time, mean time to resolve, FTE gained, and time saved. Beside it, ranked lists of the top risky users and top risky assets, each with a risk score and a 24-hour trend.
User Views
SOAR automation summary
UEBA: top risky users
UEBA: top risky assets

Know where sensitive data lives, and which of it is exposed

An overview of files, data volume, and users with PII, PHI, and PCI counts. Data is classified by risk, with data-at-risk, incorrectly classified data, and high-risk users each linking to recommendations. Compliance monitoring tracks regulated data and redundant, obsolete, and trivial files, and scan status shows coverage by source, type, and size.
User Views
Overview
Data classification
Data at risk
Compliance monitoring
Scan status

Every reported email, triaged and tracked

A 30-day summary of reported emails against true positives and clean results, with malicious elements and activity types such as phishing, targeted credential theft, and spam. An incident history chart shows trends, and a filterable log lists each incident with its threat category, resolution, and reporter.
User Views
Report summary
Malicious elements
Activity type
Incident log
SentinelOne company logo with stylized shield icon to the left of the text.
AT A GLANCE

Which Question Each Integration Answers

Integration
Category
Question it answers
Headline views
Microsoft Defender
Endpoint security
How healthy and covered are our endpoints?
Graded executive report, scorecard, coverage gaps
Splunk Premium
SIEM, SOAR, UEBA
What is automation saving us, and who is riskiest?
VisionX
Automation summary, risky users, risky assets
Forcepoint DSPM
Data security
Where is sensitive data, and is it exposed?
VisionX
Classification, data at risk, compliance monitoring
NoPhish
Email protection
What was reported, and what was malicious?
Report summary, activity types, incident log
EXPLORE THE MODULES INSIDE VISIONX

Your risk, and the Stack Behind it

VisionX Application

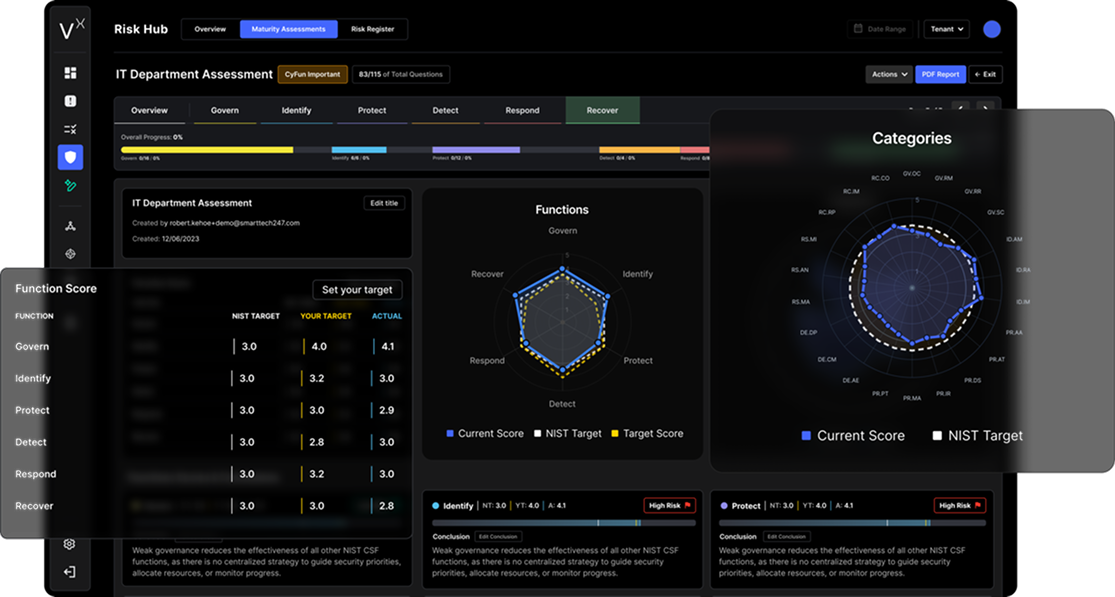
Maturity assessments, a living risk register, and human-written recommendations, so governance is something you monitor, not something you scramble for once a year.
Maturity assessments
Risk register
Benchmark advisor

VisionX Risk Hub

Maturity assessments, a living risk register, and human-written recommendations, so governance is something you monitor, not something you scramble for once a year.
Microsoft
Crowdstrike
SentinelOne
Splunk
VISIONX FAQs

Common Questions We Get Asked

Is the 319% ROI figure something we can expect too from VisionX?

It's what Forrester modelled for one customer's environment and deployment scale, not a guarantee. Your result depends on your current tooling, headcount, and incident history. We're happy to build a tailored estimate using the same framework.

Does the AI make decisions on its own within VisionX?

No. AI drafts the summary and queues the response, but a Smarttech247 analyst reviews and approves every report and every action before anything reaches you or runs against your environment. You get the speed of automation with a human still accountable for the call.

Can we keep our current SIEM or EDR with VisionX?

Yes. VisionX is technology-agnostic by design. We integrate with your existing SIEM, EDR, or XDR platform for faster onboarding and to protect the investment you've already made. There's no need to rip and replace unless you want to.

What makes VisionX different from other MDR platforms?

VisionX is built proactive and intelligence-led, not just alert triage. We combine advanced detection, automated response, and human-led analysis, backed by 24/7 SOC operations. What sets us apart is how deeply we integrate into your existing stack, the real-time visibility we give you, and threat intelligence that's tailored to your business context.

We already have an internal security team, is VisionX still a fit?

Yes, and most of our clients do. VisionX is designed to extend your internal team, not replace it. Your team retains full visibility and control. What changes is the operational burden — monitoring, triage, investigation and containment are handled by our analysts around the clock, freeing your internal team to focus on security strategy, architecture and the work that actually requires their expertise. Most clients find their team becomes more effective, not redundant.

How does VisionX support our compliance obligations?

Every incident generates a structured report mapped to MITRE ATT&CK, with full audit trails for NIS2, DORA, ISO 27001, Cyber Essentials and GDPR. Your board and auditors get the evidence they need without additional effort from your team. For organisations under NIS2, VisionX supports the 24h early warning and 72h incident reporting timelines directly, with SOC analysts who understand the regulatory context, not just the technical one.

How quickly can VisionX be deployed?

Most organisations are live within 5 to 10 days. Because VisionX connects via Microsoft native APIs, there is no rip and replace and no lengthy procurement process. Onboarding includes full environment baselining, custom detection rule configuration and analyst familiarisation with your specific environment before monitoring begins.