Agentic SOC for Microsoft Security

Peer Review

Gartner brand name text logo in white with registered trademark symbol.
5-star rating
4.8

Proven Trust

Dark blue circle with two overlapping checkmarks, one green and one light blue.
ISO 27001 text with a globe outline symbol on a black background.
2025 winner badge for Cyber Security Excellence Awards with gold and black design.
Trusted Microsoft Solutions Partner for Security

VisionX Agentic SOC for Microsoft Security triages, enriches and investigates across Defender, Sentinel and Entra in parallel, so your analysts approve the response instead of chasing alerts.

Book a Demo
<15 Min

Incident Response

319% ROI

Measured by Forrester

75%

Improvement to MTTR
By now, most organisations have already
suffered significant business impact.
Microsoft Certified Security Operations Analyst Associate badge with two white stars.
THE PROBLEMS THE AGENTIC SOC ADDRESSES

Conventional SOC Wasn't Built for this Threat Landscape

Volume has outpaced human capacity

The average organisation runs 50 or more security tools. Each one generates alerts, jobs, and actions. Analysts are not investigating threats. They are triaging an inbox that never empties. The problem is not skill. It is scale.

Attacks are faster and more targeted

AI-enabled adversary operations increased 89% year on year. Attackers now move from initial access to lateral movement in under an hour. A SOC built around human triage speed was not designed for this.

CISOs must demonstrate agentic readiness

Security is no longer a back-office function. Boards want evidence that their security programme uses automation intelligently, reduces human exposure to repetitive decisions, and operates at machine speed where it matters.

Building SOC automation yourself doesn't scale

Most organisations know they need to automate. Building it themselves means months of engineering, a SOAR platform, custom playbooks, and an ongoing maintenance burden. Almost nobody finishes.
HOW WE HELP

Discover the Agentic SOC capability for Microsoft Security

Smarttech247’s Agentic SOC capability in VisionX brings AI-powered investigation, human expertise and coordinated Microsoft response together in one operational model. Built for organisations using Microsoft Security technologies, it helps teams move faster from alert to evidence, from evidence to decision, and from decision to action.
01
AI-powered investigation
Agents enrich alerts, correlate activity and surface evidence across identity, email, endpoint, user and device data.
OUTCOME
Reduces manual investigation time and helps security teams understand what happened faster.
02
Human-led decision making
Smarttech247 analysts validate findings, apply threat expertise and oversee high-impact response decisions.
OUTCOME
Enables faster security operations without losing human judgement, governance or accountability.
03
Coordinated, fast response
VisionX brings investigation timelines, affected entities and response actions into one operational hub.
OUTCOME
Coordinates actions such as session revocation, MFA resets, endpoint scans, file quarantine and device isolation across the Microsoft security stack.
LEGACY SOC VS AGENTIC SOC

Different Timelines. Different Outcomes

Traditional SOC Workflows Can’t Match AI-Powered Attacks
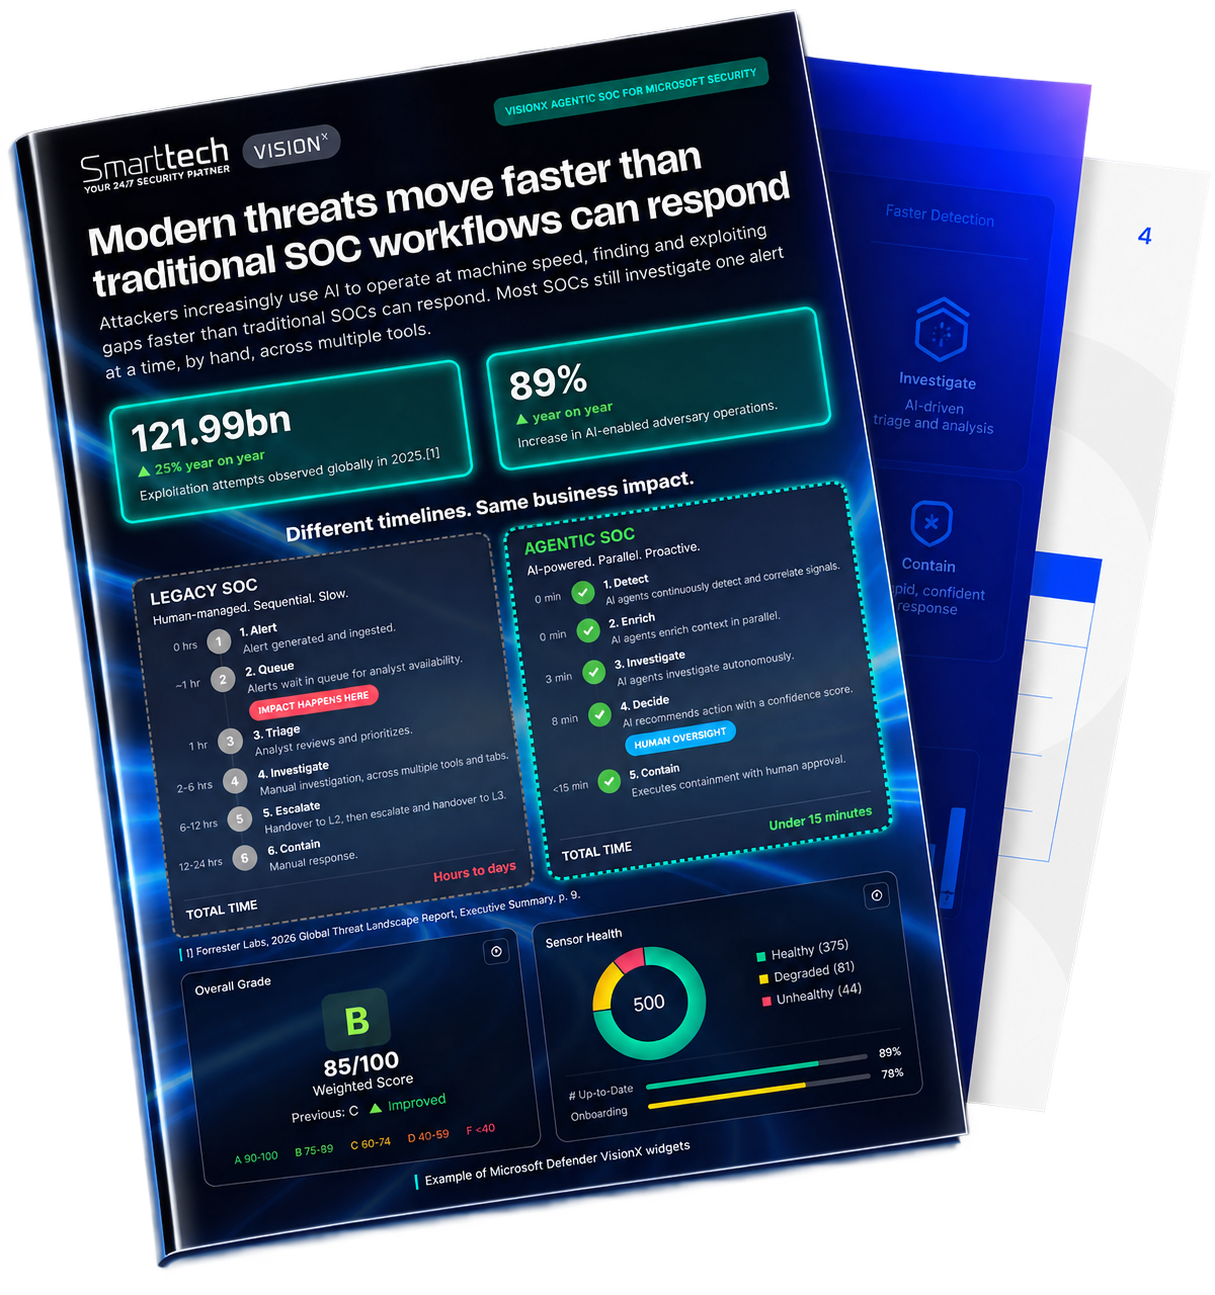
In a legacy SOC, every alert waits for an analyst. Triage, investigation and escalation happen one step at a time, across multiple tools and tabs, and containment can take hours or days. The gap between detection and response is where the business impact happens.
0 hrs
1. Alert
Alert generated and ingested.
~ 1 hr
2. Queue
Alerts wait in queue for analyst availability.
~ 1-2 hrs
3. Triage
Analyst reviews and prioritises.
~ 2-6 hrs
4. Investigate
Manual investigation, across multiple tools and tabs.
~ 6-12 hrs
5. Escalate
Handover to L2, then escalate and handover to L3.
~ 12-24 hrs
6. Contain
Manual response.
Total Time
Hours to days
AGENTIC SOC

AI-Powered. Parallel. Proactive

Agentic SOC for Microsoft Security: AI-Powered Investigation with Human Approval
AI agents detect, enrich and investigate in parallel, then recommend an action with a confidence score. An analyst approves it before containment executes. The queue is removed and human judgement stays in control.
0 min
1. Alert
AI agents continuously detect and correlate signals.
0 min
2. Enrich
AI agents enrich context in parallel.
5 min
3. Investigate
AI agents investigate autonomously.
8 min
4. Decide
AI recommends action with a confidence score.
< 15 min
5. Contain
Executes containment with human approval.
Total Time
Sub 15 minutes
INVESTIGATION HUB

Lock Compromised Devices in a Single Step

The query runs, results return as actionable entities, response actions unlock scoped to all of them. Press run to see the chain.
Case #MS-2847 · Defender for Identity
High
Confirmed
Suspicious sign-in + credential access attempt
Source Defender for Identity
MITRE T1078 · T1110
Opened 2 mins ago
AI verdict
j.brennan@acme.com shows sign-in from Dublin and Frankfurt within 11 minutes. MFA bypassed on second session. Likely compromised credential. Immediate action recommended.
Affected entities
j.brennan@acme.com
Finance · Global Admin
Frankfurt, DE
Anomalous location
Investigation hub
Device ownership lookup
3 devices found
RDP access check
Login history · last 48h
Device ownership — 3 devices found for j.brennan@acme.com
ACME-WIN-0042
‍
Windows 11 · Last seen 4 mins ago · Dublin
ACME-WIN-0091
Windows 11 · Last seen 2 days ago · Cork
ACME-WIN-0042
‍
Windows 11 · Last seen 4 mins ago · Dublin
Response actions: Select actions to execute
Reset MFA
j.brennan@acme.com
Revoke all sessions
j.brennan@acme.com
Isolate all 3 devices
WIN-0042 · 0091 · MBP-0017
Lock account
j.brennan · Entra ID
Query runs against Entra ID and Defender. Results return as pre-selected device entities. Response panel unlocks scoped to the user and all found devices. One action contains all three.
WHAT POWERS THE TEAM

The Operational Layer for Microsoft Security

Ready to go platform

VisionX is built and running on the Microsoft security stack today. No months of implementation, no waiting on a roadmap. You get enriched, triaged, correlated data from day one of onboarding.

SOAR and AI Included

Automation and agentic AI aren't an add-on you have to buy or build. They're part of the platform, running across every customer, getting better continuously. No Logic Apps to maintain, no in-house SOAR project to fund.
CLIENT OUTCOMES

What Our Clients Say About Us

MDR FOR MICROSOFT SECURITY

What to Ask Before Choosing an MDR for Microsoft

How can we prove Microsoft expertise?

The Microsoft credentials and integrations behind our detection and response.

Need Microsoft Security expertise?

Our analysts monitor and respond across your Microsoft stack around the clock.

What should we ask in a Microsoft tender?

The Microsoft credentials and integrations behind our detection and response.
Agentic SOC for Microsoft

Microsoft Security Enhanced by AI

Smarttech247 runs your Defender, Sentinel, and Entra stack as a single operational system. Our agentic soc uses AI-powered investigation. Human-authorised response. No new tools required.

Microsoft Solutions Partner

Talk to someone who understands agentic security operations

Have a direct conversation about your environment with a member of our team.
How AI-led investigation reduces analyst workload
Where automation runs, where human judgement takes over, and how that split is governed in practice.
What this looks like inside your Microsoft stack
Specific to Defender, Sentinel, and Entra
Whether your environment is ready
An honest assessment of what is needed to operationalise agentic response across your current setup.
BEFORE YOU BOOK THE CALL

FAQs About the Agentic SOC for Microsoft

What does the Agentic SOC actually do during a Microsoft security incident?

It orchestrates the full investigation and remediation workflow across your Microsoft security stack, including Defender for Endpoint, Defender for Identity, and Defender for Email. Rather than an analyst switching between multiple tools, everything is surfaced in one interface, with enrichment, investigation, and response actions all executed from a single hub.

What response actions are available for Microsoft environments?

For users: reset MFA, reset password, revoke active sessions, and lock or unlock accounts. For devices: run a scan, quarantine files, or isolate the device from the network entirely. These actions are triggered directly from within the investigation hub.

Does the Agentic SOC only work with Microsoft tools?

Microsoft is the current focus because it covers the majority of customer environments. Splunk is next on the roadmap, followed by other SIEMs and EDRs. The platform is built so that integrations with additional vendors (CrowdStrike, Okta, etc.) can be added without rebuilding core capabilities.

Do I need to pay for CoPilot to use this?

No, we do not use CoPilot as part of this. At Smarttech247 we have our own SOAR and AI system that is embedded in VisionX

How does this connect to what customers see in VisionX?

All enriched incident data, analyst context, and investigation timelines are pushed directly into VisionX in real time. Customers get end-to-end visibility: from alert ingestion through investigation and remediation, all surfaced in the platform they already use for security reporting.

Why can't a customer's internal team just build this themselves?

The complexity is the barrier. Automation requires deep understanding of how each tool works, how data normalises across sources, and how to safely execute response actions at scale. Most organisations, based on their own assessments, still don't have full visibility into their environments, let alone the foundations needed to automate across them. Smarttech247 absorbs that build cost once and delivers it across all customers.