Assess Your Security from Every Angle to Find Risk

Smarttech247’s Red Teaming services replicate advanced adversaries in controlled conditions, exposing how resilient your organisation truly is when faced with sophisticated threats.

Peer Review

Gartner brand name text logo in white with registered trademark symbol.
5-star rating
4.8

Proven Trust

Dark blue circle with two overlapping checkmarks, one green and one light blue.
ISO 27001 text with a globe outline symbol on a black background.
2025 winner badge for Cyber Security Excellence Awards with gold and black design.
Offensive Security:
Awards Image

ISO 27001

Awards Image

Cyber Essentials

Awards Image

Tech Excellence

Assess Your Organisation's Threat Detection and Response Capabilities

Red teaming goes beyond traditional penetration testing by assessing how well your organisation can detect, respond to and recover from a determined attacker. Smarttech247 replicates genuine adversary behaviour across people, processes and technology to expose weaknesses that routine testing simply cannot reveal.

Full-Spectrum Attack Simulation

We emulate real adversaries across physical, human and technical vectors to uncover weaknesses in your overall security posture, not just your systems.

Detection and Response Evaluation

Our engagement measures how quickly and effectively your SOC, IR teams and controls detect suspicious activity, privilege abuse and attempted data exfiltration.

Multidisciplinary Security Assessment

From social engineering and physical access attempts to technical exploitation, we analyse every angle to identify gaps in processes, human behaviour and technology.

Targeted Red Teaming Capabilities That Reveal Real-World Weaknesses

Our red team operations simulate genuine adversaries to uncover how your people, processes and technology hold up under pressure. These exercises expose hidden attack paths, validate defensive effectiveness and give you the evidence needed to strengthen long-term resilience.

Evaluate Response Readiness

Expose exploitable gaps across people, processes and technology that attackers rely on.

Identify Security Weaknesses

Expose exploitable gaps across people, processes and technology that attackers rely on.

Uncover Hidden Paths to Compromise

Reveal multi-step attack routes and misconfigurations that traditional testing never touches.

Assess Defensive Team Performance

Measure how well blue teams react to adversary tradecraft instead of predictable test scenarios.

Prioritise High-Impact Improvements

Use evidence from red team operations to focus investment on the controls that genuinely strengthen resilience.

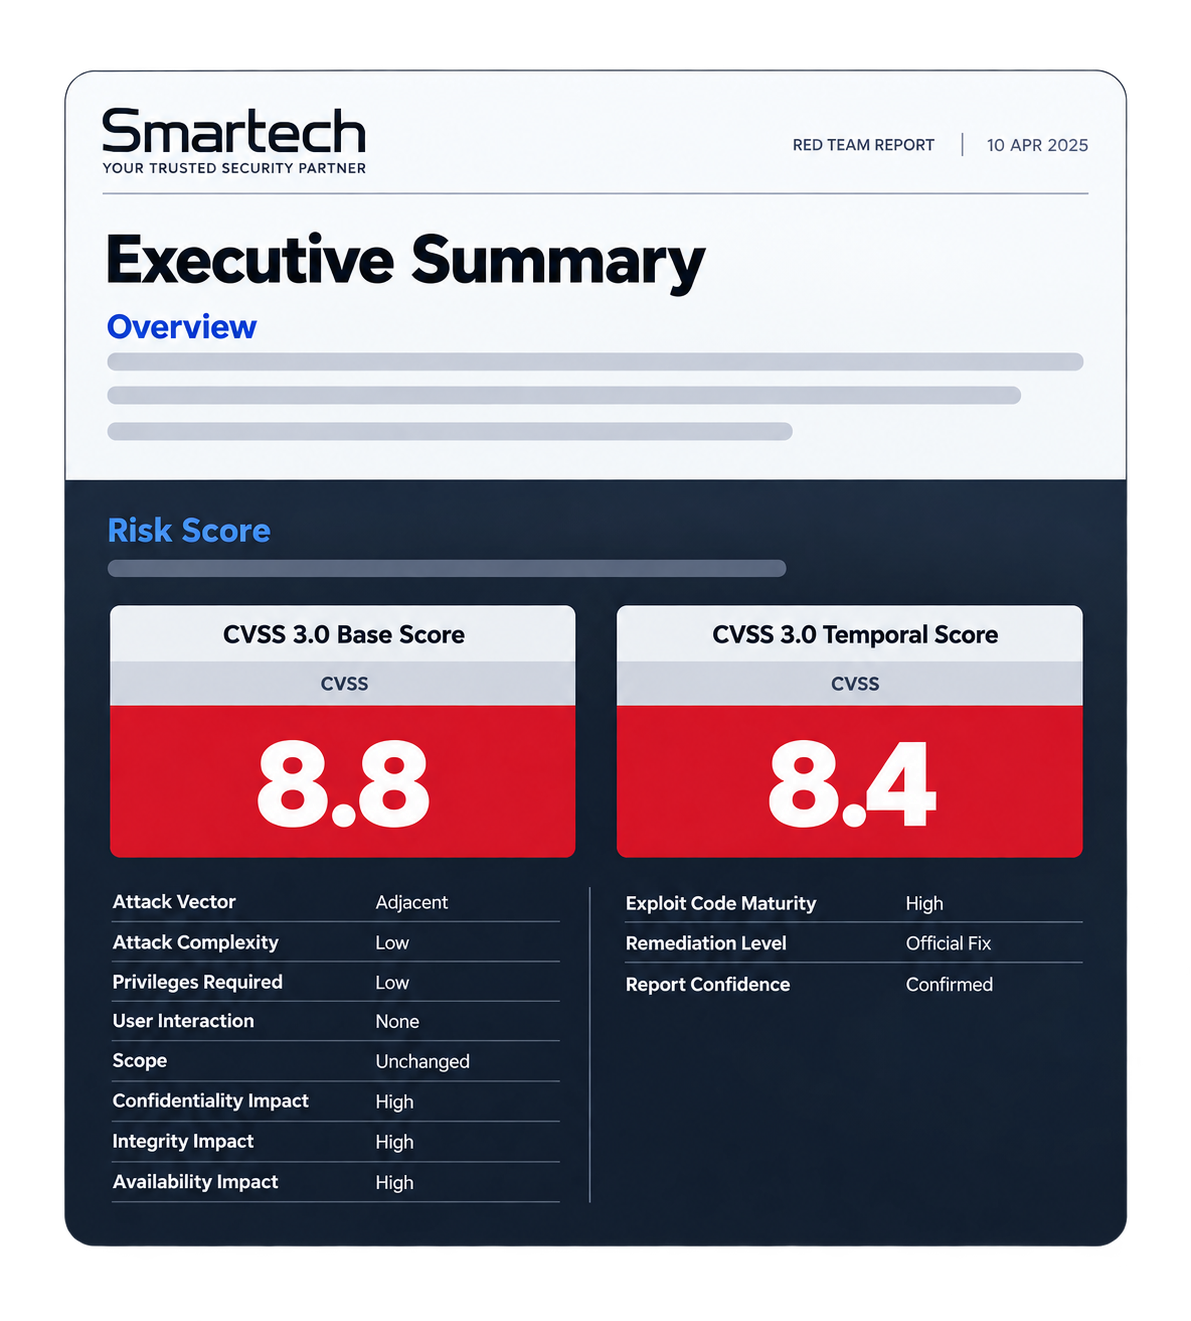
Dashboard mockup

Why Organisations Turn to Red Team Penetration Testing

Most teams don’t know how exposed they really are. Security tools give a false sense of safety, internal testing is predictable and attackers don’t follow rules. Red team penetration testing cuts through that uncertainty by showing where your defences actually break, how far an intruder could get and what the consequences would be if someone with intent targeted your organisation.

You Don’t Know Your Real Attack Surface

Shadow assets, misconfigurations and forgotten systems create gaps no one sees until an adversary does.

Your Defences Might Not Trigger When It Matters

Alerts look fine during audits, then fail silently when an attacker uses techniques your tools weren’t tuned to catch.

Leaders Need Proof, Not Assurances

Red team results give hard evidence of what an attacker can reach so decisions aren’t based on guesswork or optimism.

Small Weaknesses Become Big Compromises

Minor oversights chain together into full-scale breaches, and red teaming reveals those escalation paths before someone weaponises them.

Expertise That Shows You the Truth

Our specialists bring the same mindset, techniques and discipline used by real adversaries. We understand how attackers chain weaknesses, bypass controls and quietly escalate access, and we translate those behaviours into clear, evidence-driven guidance your teams can act on. You get a level of insight that traditional testing never uncovers.
Support

Everything You Need to Know Before You Decide

Here you’ll find clear answers to the most common questions we hear from security and IT teams.

If you need anything more specific, we’re always here to help.
Do you just alert us, or do you act?
We contain, investigate, and support recovery. You get outcomes, not notifications.
Will we work with named analysts we know?
Yes. A human-driven partnership with white-glove communication and high-touch support.
How do you prove what happened?
Chain of custody, audit trails, and executive-ready reporting you can trust.
Can you cover both IT and OT?
Yes. One coordinated team across your entire estate, including sector-aware context.
How do you improve our security over time?
Every incident yields new detections and hardened controls that reduce repeat risk.

Ready to scale your security and compliance operations?

We protect your on-premise/cloud/OT environments - 24x7x365

We Simulate Real-World Attacks on Your Organisation

Peer Review

Gartner brand name text logo in white with registered trademark symbol.
5-star rating
4.8

Proven Trust

Dark blue circle with two overlapping checkmarks, one green and one light blue.
ISO 27001 text with a globe outline symbol on a black background.
2025 winner badge for Cyber Security Excellence Awards with gold and black design.

We simulate a real adversary against your organisation, then show you what they reached, what went undetected, and how your team responded.

Talk to our team

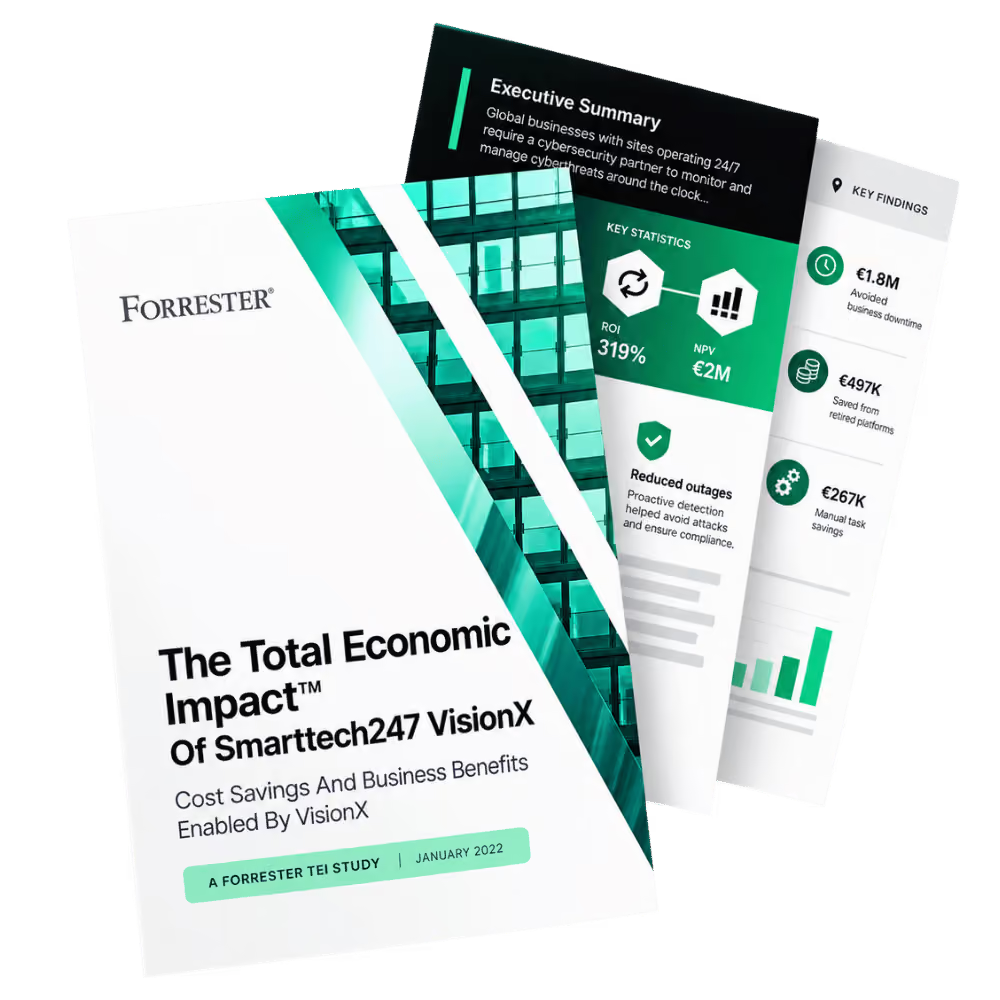
319% ROI

Independent ROI Study

<6 Months

Payback

€2M

Net Present Value
By now, most organisations have already
suffered significant business impact.
ATTACK VECTORS

Real Attackers Try Every Way In

A red team can test several routes at once.
You see how technical and human weaknesses combine.
Technical systems
Can an attacker break in and move through your environment?
Social engineering
Do your staff spot and report a convincing approach?
Insider threats
What could a trusted person with access reach, and would it be noticed?
Physical Security
Can someone walk past the controls on your buildings and devices?
YOU SET THE GOAL

Choose Your Mission

Every exercise is built around the outcome that worries your business most. Pick one to see how we frame it.
Can an attacker get in and keep access?
You can't give the board a straight answer when your risk lives across five different consoles. VisionX pulls telemetry from your SIEM, EDR, network, identity, and cloud into one picture, so you always know where you stand.
STARTING POINT
From outside, with no access.
ATTACKER GOAL
Gain access and keep it without being found.
WE MEASURE
Whether your SOC spots the foothold, and how soon.
Start from inside
You can't give the board a straight answer when your risk lives across five different consoles. VisionX pulls telemetry from your SIEM, EDR, network, identity, and cloud into one picture, so you always know where you stand.
STARTING POINT
From inside, with access already granted.
ATTACKER GOAL
See how far an attacker can get from a foothold.
WE MEASURE
How quickly movement is detected and your team responds.
Change Active Directory
You can't give the board a straight answer when your risk lives across five different consoles. VisionX pulls telemetry from your SIEM, EDR, network, identity, and cloud into one picture, so you always know where you stand.
STARTING POINT
Agreed with you at the start.
ATTACKER GOAL
Change Active Directory.
WE MEASURE
Whether the change is seen and the right playbook runs.
Take data out
You can't give the board a straight answer when your risk lives across five different consoles. VisionX pulls telemetry from your SIEM, EDR, network, identity, and cloud into one picture, so you always know where you stand.
STARTING POINT
Agreed with you at the start.
ATTACKER GOAL
Take agreed data out of your environment.
WE MEASURE
Whether the data leaving is detected, and how fast you act.
WHAT YOU GET

What's in Every Report

Here is how we present the results of an engagement.
This excerpt is illustrative onlynd human weaknesses combine.
How each attack was executed
A clear account of what the adversary did, step by step.
What went undetected
The activity your tools and team did not catch.
How your SOC performed
Detection, response time against SLAs, and playbook use.
Recommendations
Clear improvements for your security team.
RED TEAM OR PEN TEST?

Red Team Goes Beyond Pentesting

Penetration Testing
Red Team Exercise
The question
VisionX
What technical flaws do we have?
Can an attacker reach their goal, and would we notice?
The approach
Finds vulnerabilities
Uses stealth, persistence and evasion to avoid detection
Who is tested
Systems and configurations
Security personnel, incident response plans and controls
The outcome
Issues to patch
How attacks ran, what went undetected, how your team responded
Best for
Compliance and patching
Mature teams who want to push their defences to the limit
SentinelOne company logo with stylized shield icon to the left of the text.
BUILT AROUND HOW YOUR TEAM WORKS

VisionX Shows Each Role Exactly What They Need

Your queue, prioritised
You open 10 tabs just to work out which alert is actually a P1. VisionX hands you your queue already prioritised, P1s first, with the context attached, so you act on an incident instead of guessing at an alert.
P1
Lateral movement, HOST-012
P2
Credential theft attempt
P3
Policy violation, flagged
Your team's performance, over time
VisionX tracks triage rates, MTTA and MTTR by priority over time, so you can show leadership your team is handling more scale without more headcount.
ANALYST TIME ON REAL INVESTIGATIONS
62%
illustrative only, not a sourced figure
Your risk posture, over the long term
The board doesn't want to hear about yesterday's incident. It wants to know if you're actually getting safer. VisionX tracks your maturity over time and turns it into board-ready reporting, so you can answer that question with a trend, not a guess.
74
POSTURE SCORE
illustrative trend
exportable as board PDF
HOW IT WORKS

From Agreed Goal to Usable Report

You choose the objective that reflects your biggest concern, and we agree what success looks like for the attacker.

We act as a real adversary, using stealth, persistence and evasion to avoid detection.

We record what your SOC detects, how quickly it responds and whether the playbook runs correctly.

You receive a detailed report on how the attacks ran, what went undetected, and what to improve.
STEP 1
Agree the goal
STEP 2
Simulate the attack
STEP 3
Measure your response
STEP 4
Report and recommend
EXPLORE THE MODULES INSIDE VISIONX

Your risk, and the Stack Behind it

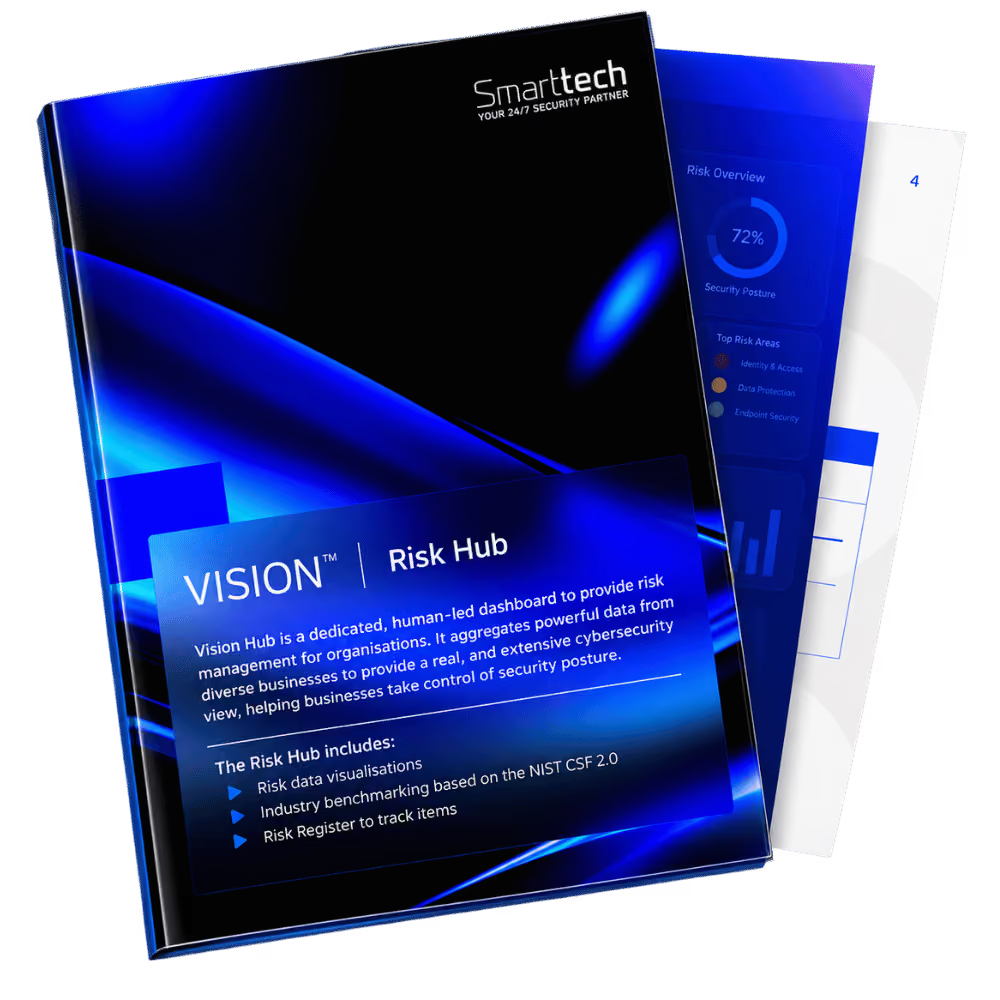
VisionX Risk Hub

Maturity assessments, a living risk register, and human-written recommendations, so governance is something you monitor, not something you scramble for once a year.
Maturity assessments
Risk register
Benchmark advisor

Technology Integrations

Keep the tools you've already invested in. VisionX runs on top of your SIEM, EDR, and XDR platforms and gives you one view across all of them.
Microsoft
Crowdstrike
SentinelOne
Splunk
Featured manufacturing case study
Global Metal Packaging Manufacturing

Trivium Packaging Case Study

7, 200

Employees

57

Locations globally

50

Manufacturing plants
Roel Schouten
Vice President Information Security
"If they discover a high-confidence attack at 3 o'clock in the night, they can isolate the system, no matter how critical the system is. I don't have 24/7 coverage in my team. It's good to have someone there that we know is helping us around the clock."

Customer Challenges

Trivium Packaging manufactures cans and aerosols across 57 locations and roughly 50 plants globally. The business runs on uptime, and ransomware groups know it: disrupt output, extract a ransom. Trivium learned this in 2021 after an enterprise-wide ransomware attack.

Trivium's internal security team is lean, around 10 people, spread across Europe and the US, with no way to sustain 24/7 coverage on their own. An attack at 3am doesn't wait for business hours.

Customer Challenges

Smarttech247 gives Trivium round-the-clock coverage its own team can't sustain, with authority to isolate a compromised system the moment a high-confidence attack is detected, no approval call required.

The Results

0

Critical incidents

1,401

Threats caught

80%+

More phishing reports,
‍zero drop in accuracy
VISIONX PRODUCT GUIDES

Get More Details Behind VisionX

Three guides, one for Microsoft-specific SOC automation, one for core MDR, one for Risk Hub. Download the one that matches what you're actually evaluating.

VisionX Risk Hub Product Guide

VisionX Risk Hub gives organisations one place to assess, track and visualise cybersecurity risk, built on NIST CSF 2.0 maturity benchmarking.

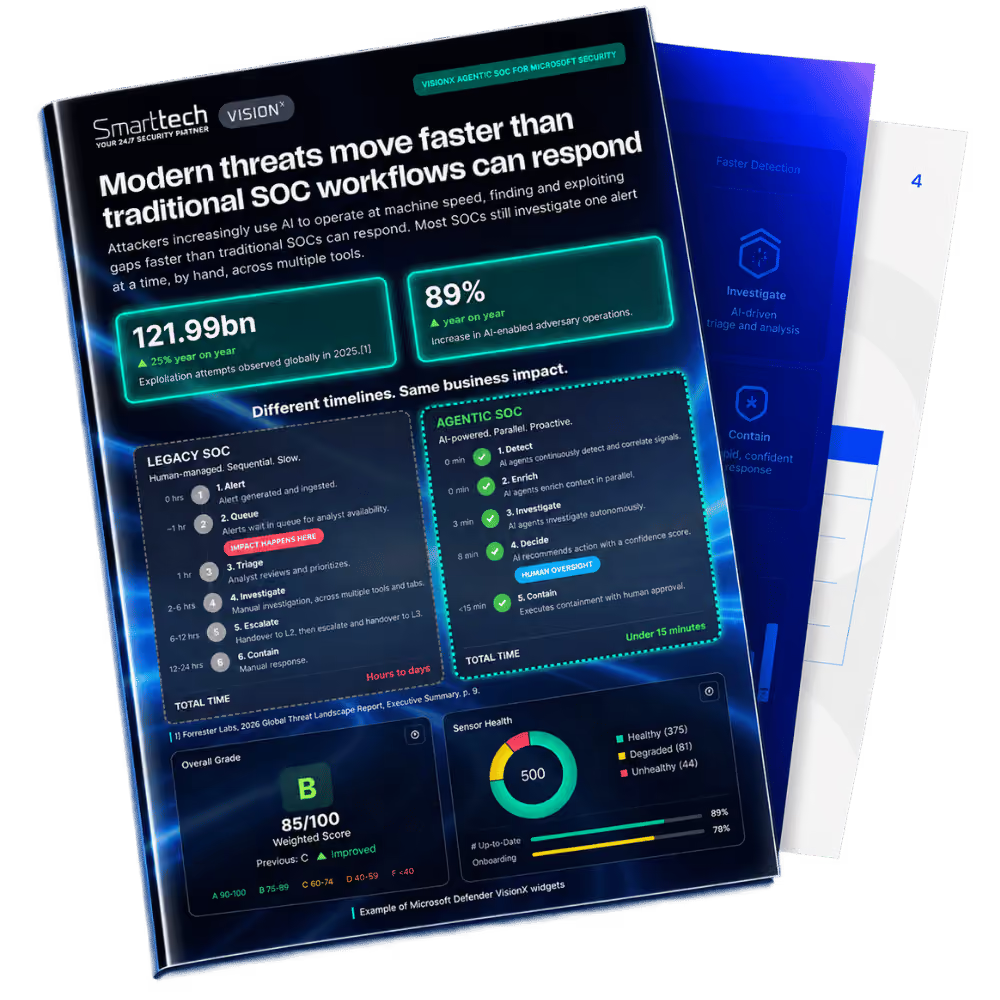
VisionX Agentic SOC for Microsoft Security

Transform Microsoft security operations with VisionX Agentic SOC. Automate triage and investigation, target sub-15-minute response, and retain human oversight for critical actions.

VisionX MDR Product Guide

VisionX MDR delivers 319% ROI in under 6 months and 50% risk reduction in the first 180 days, with active defence in under 15 minutes.

Why the Organisation Chose Smarttech247

The manufacturer had grown through acquisition, leaving fragmented security tooling and no incident response process in place. VisionX consolidated this into 24/7 monitored coverage, deployed country-by-country starting with a two-week rollout to the first site.
  • Detected the WannaCry ransomware incident early, before it caused damage
  • Replaced ad hoc security checks with continuous monitoring
  • Gave board-level visibility into risk posture for budget decisions
VISIONX FAQs

Common Questions We Get Asked

No items found.