

Microsoft Security Solutions Partner


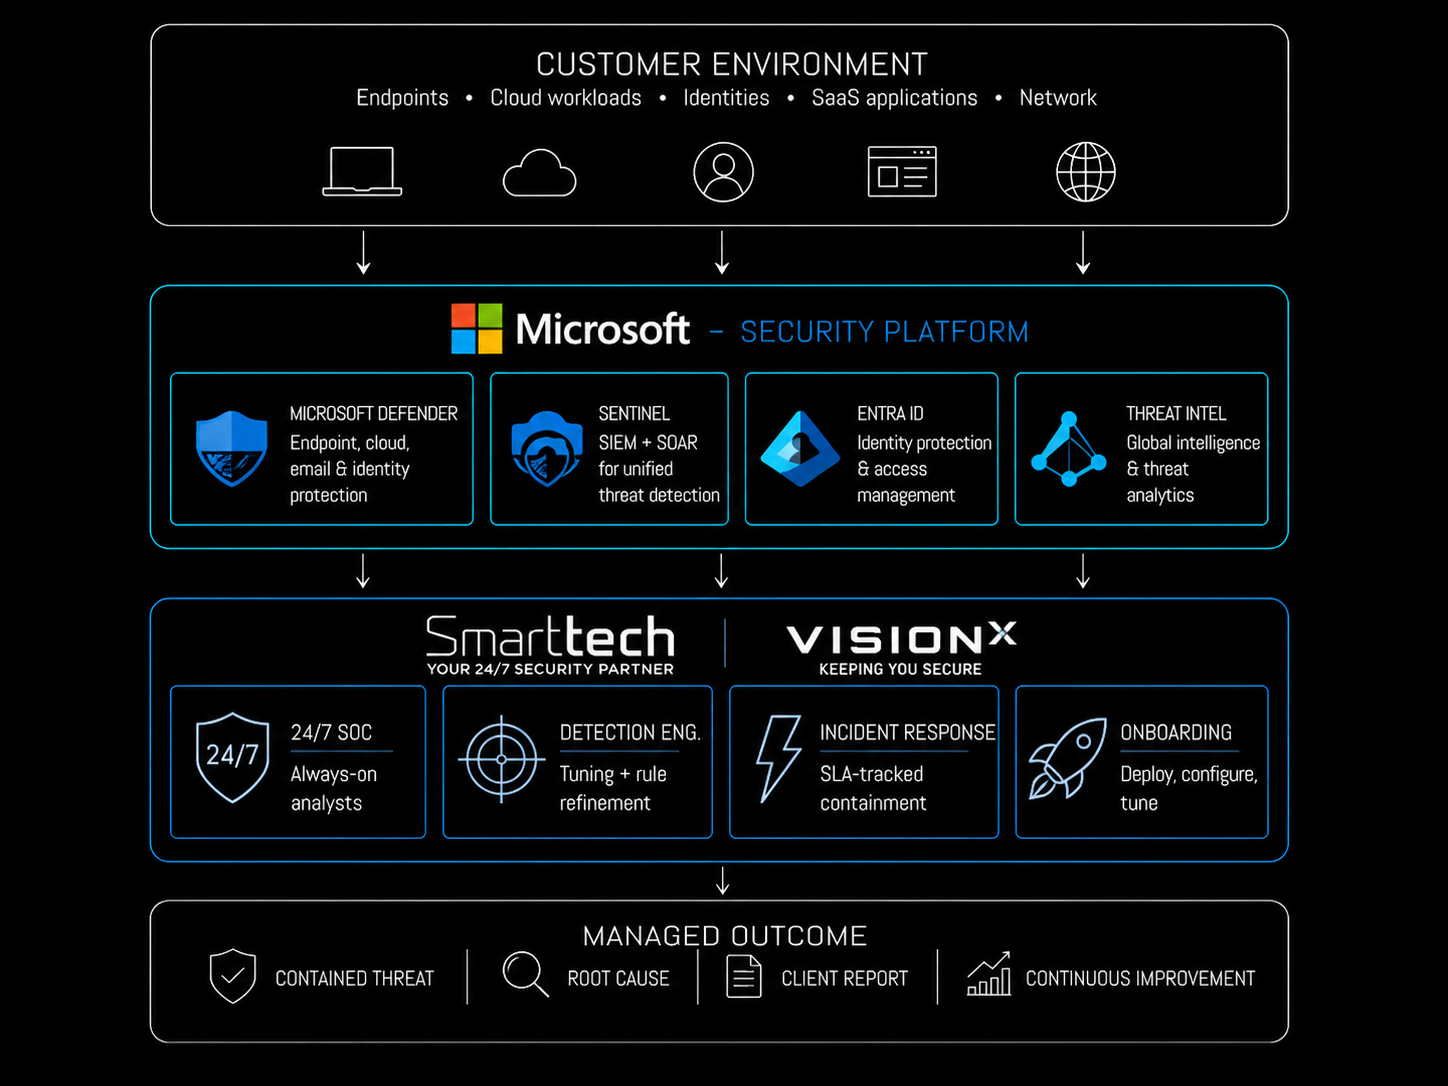
Smarttech247 is a Microsoft Security Solutions Partner. Our certified analysts run 24/7 managed detection and response across Defender, Sentinel and Entra, so you get full value from your Microsoft investment without the operational burden.
Talk to us<15 Min
319% ROI
75%

What Microsoft Partner Status Means for You
Sentinel, managed and tuned
Detection and response in one service
Expertise others have recognised
Support where you operate
Hear from Our CRO About Getting More from Microsoft

One Service Across Your Microsoft Stack
See What We Cover
Microsoft
Sentinel
Defender
XDR
Microsoft
Entra ID
Defender
for Cloud

Defender
for Office365
Proven MDR Outcomes
What to Ask Before Choosing an MDR for Microsoft

How does the SOC actually Respond?
Need Microsoft Security expertise?

What should we ask in a Microsoft tender?
Microsoft Solutions Partner
Talk to someone who understands agentic security operations
Your Questions About Microsoft and Smarttech247
What compliance frameworks does the Smarttech247 Microsoft MDR service support?
Microsoft’s native audit logs, compliance workbooks, and security reporting capabilities directly support a range of regulatory frameworks. Smarttech247’s managed service on top of Microsoft Sentinel and Defender XDR helps organisations build and maintain evidence for GDPR Article 32 (technical security measures), NIS2 incident detection and reporting obligations, DORA’s operational resilience and ICT incident management requirements, and ISO27001 Annex A controls. Our SOC team can tailor reporting and alert workflows to align with the specific evidence requirements of your regulatory environment. If you have a specific framework in mind, we will confirm coverage during the onboarding scoping call.
Can Smarttech247 work alongside our existing Microsoft partner or reseller?
Yes. Smarttech247 operates as the managed security layer on top of your Microsoft environment and does not conflict with existing Microsoft licensing partners or resellers. Many clients work with a Microsoft partner for licensing, procurement, and productivity workloads while using Smarttech247 specifically for security operations — monitoring, detection, and incident response. We are happy to engage directly with your existing Microsoft partner to ensure a clean handover and avoid duplication of effort during onboarding.
How quickly can Smarttech247 get our Microsoft environment live under managed coverage?
Microsoft-centric environments are typically live within five business days of engagement. Because most organisations are already operating within the Microsoft ecosystem, there is no need for new agents or significant infrastructure changes. Smarttech247 handles ingestion configuration, initial detection rule tuning, and log source verification during onboarding — your team does not need to manage the technical setup. Larger or more complex environments with multiple Azure tenants or hybrid on-premises infrastructure may require additional time, which we scope during the initial discovery call.
Do you manage Microsoft Sentinel or replace it with your own SIEM?
Smarttech247 manages Microsoft Sentinel — we do not replace it. Our SOC team operates your Sentinel workspace directly, handling ingestion configuration, analytic rule development using KQL, watchlist management, playbook development, and ongoing false positive reduction. Sentinel remains your SIEM; Smarttech247 adds the 24/7 analyst expertise, detection engineering, and SLA-tracked incident response that makes it effective around the clock. For clients already running Sentinel, we layer our managed service on top of the existing deployment without disruption.
What Microsoft licences do I need to use Smarttech247 MDR?
You do not need to purchase additional licences to get started. Smarttech247 MDR is designed to unlock the security capability already included in Microsoft E3 and E5 licences — tools like Microsoft Sentinel, Defender XDR, Entra ID, and Defender for Cloud. Many organisations are already paying for these but are not using them to their full potential. Smarttech247 handles the configuration, tuning, and 24/7 monitoring on top of your existing licensing investment. If gaps exist in your current licensing, we will identify them during onboarding and advise on the most cost-effective path forward.