24/7 MDR for Your Microsoft Security Stack

Peer Review

Gartner brand name text logo in white with registered trademark symbol.
5-star rating
4.8

Proven Trust

Dark blue circle with two overlapping checkmarks, one green and one light blue.
ISO 27001 text with a globe outline symbol on a black background.
2025 winner badge for Cyber Security Excellence Awards with gold and black design.
Trusted Microsoft Solutions Partner for Security
A 24/7 managed detection and response service for your Microsoft security stack. Our analysts investigate and contain threats in your Defender, Sentinel and Entra environment, backed by our AI detection and automation.

<15 Min

Incident Response

319% ROI

Measured by Forrester

24/7

AI Powered. Human-Led
By now, most organisations have already
suffered significant business impact.
Microsoft Certified Security Operations Analyst Associate badge with two white stars.
HOW OUR SERVICE WORKS WITH MICROSOFT

Expert Depth. Machine Speed. Human Accountability

Microsoft E3 and E5 licences include powerful security capabilities that most organisations only use at a fraction of their potential. VisionX activates every capability you're already paying for and makes it work for you around the clock. Our service is built on a decade of frontline incident response experience, designed from the ground up for organisations that run on Microsoft.
Trained on millions of Microsoft events
Our detection engineers write and tune Sentinel analytics rules and hunting queries for your environment. Our AI models, trained on millions of Microsoft security events, score and correlate alerts, cutting alert noise before an analyst needs to look.
Automated playbooks act in seconds
When a confirmed threat is identified, our analysts run pre-approved SOAR playbooks that act in seconds, isolating hosts via Defender for Endpoint, revoking Entra ID sessions, blocking malicious IPs, and quarantining emails, all without waiting for manual approval.
Certified Microsoft analysts for validation
Our certified Microsoft analysts provide judgement, validating complex attack chains, conducting proactive threat hunts inside your Sentinel workspace, and delivering post-incident analysis that turns every event into a stronger defence.
Certified Microsoft Security Partner
Smarttech247 holds Microsoft Solutions Partner status for Security, giving our team direct access to Microsoft's threat intelligence feeds and security programmes, and providing our customers with a structural advantage in detection speed and product depth.
FULL-SPECTRUM COVERAGE

From Endpoint to Cloud. Every Signal, Always On

VisionX MDR connects natively to your Microsoft ecosystem, ingesting signals across every layer of your environment so threats can never hide between the cracks.

Endpoint

Microsoft Defender for Endpoint
Behavioural threat detection, live response, automated isolation, and host containment, stopping attackers from pivoting after initial compromise

Identity

Microsoft Defender for Identity
Real-time monitoring of Active Directory and Entra ID for credential abuse, lateral movement, and privilege escalation attempts.

Email & Collaboration

Defender for Office 365
Detection and takedown of phishing campaigns, business email compromise, and malicious attachments across Microsoft 365 collaboration surfaces.

Cloud Apps

Defender for Cloud Apps
Shadow IT discovery, anomalous access detection, and policy enforcement across SaaS applications connected to your tenant.

Cloud Infrastructure

Microsoft Defender for Cloud
Continuous posture assessment, misconfiguration remediation, and workload protection across Azure, multi-cloud, and hybrid environments.

SIEM & XDR

Microsoft Sentinel
Custom detection engineering, analytics rules, and threat hunting queries built on Sentinel and enriched with Smarttech247's proprietary threat intelligence.

IoT & OT Security

Microsoft Defender for IoT
Agentless discovery and continuous monitoring of IoT and OT devices, protecting operational technology environments and industrial control systems from targeted attacks.
HOW IT WORKS

One Service Across Your Microsoft Stack
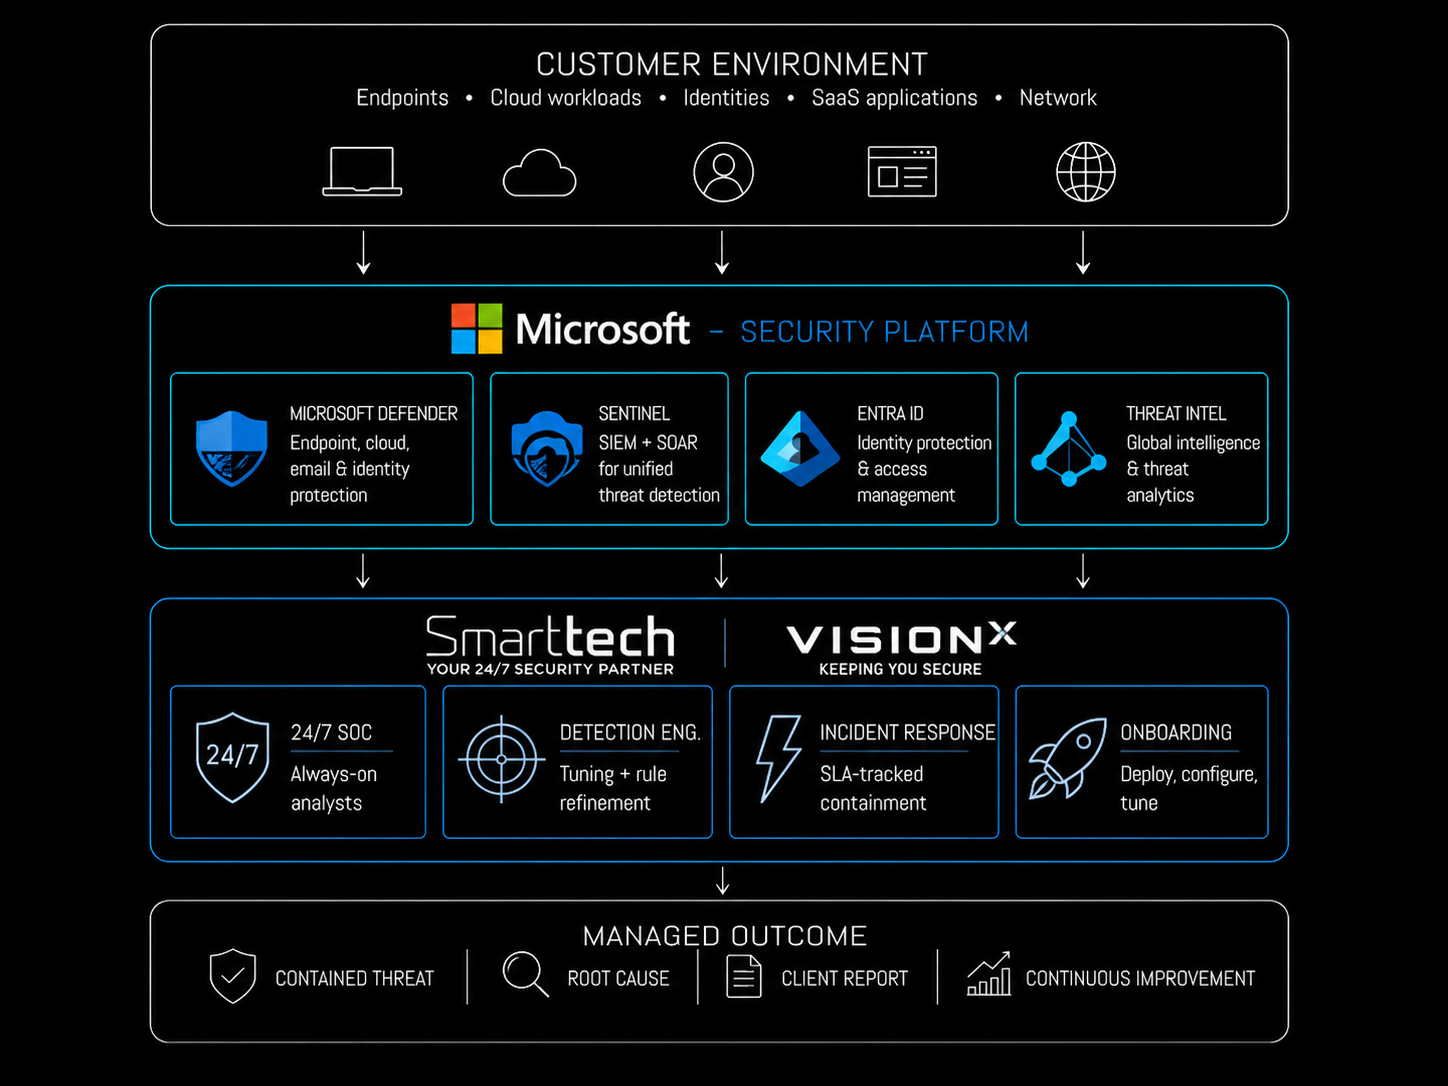
ILLUSTRATIVE INCIDENT RESPONSE TIMES FOR MDR

From Alert to Containment

Most MDR providers alert. We act. Detection engineers tuning your rules, analysts hunting threats your tools never flagged, and a response team that contains incidents in minutes. Every discipline feeds the next.
3:45pm
Potential ransomware threat detected
Suspicious activity identified through continuous monitoring. The incident is immediately prioritised for investigation.
3:49pm
Incident escalated and response activated
Security specialists assess the threat, activate the agreed response plan and notify key stakeholders.
3:54pm
Threat contained to minimise disruption
Immediate containment measures limit further exposure and protect critical business operations.
3:58pm
Ransomware controlled · blast radius: one server
13 min
The incident is contained to a single server, with no further spread identified. Investigation and recovery planning begin.
Incident contained — sub 15 minutes
Rapid response limited the incident's scope. Stakeholders are informed, evidence is preserved and a post-incident review is initiated.
Incident Response
NOT ALL MDR IS EQUAL

We Don't Just Alert You. We Take Action

Many providers claim to support Microsoft environments. VisionX goes further by delivering complete, hands-on response that most vendors leave to your internal team.
Capability
VisionX MDR
Typical MDR
24/7 Security Event Monitoring
Threat Detection Across Defender XDR
Partial
Custom Microsoft Sentinel Detection Engineering
Host isolation under pre-approved playbooks
Identity Threat Response (Entra ID / AD)
Partial
Full Incident Remediation
Proactive Threat Hunting
Proprietary Threat Intelligence
3rd-party only
Unlimited Incident Response Retainer
Certified Microsoft Security Experts On-Call
Varies
MDR FOR MICROSOFT SECURITY

What to Ask Before Choosing an MDR for Microsoft
How does the SOC actually Respond?
How automated triage and analyst-led investigation work together across your Microsoft environment.

How can we prove Microsoft expertise?

The Microsoft credentials and integrations behind our detection and response.

What should we ask in a Microsoft tender?
The Microsoft credentials and integrations behind our detection and response.

Microsoft Solutions Partner

Talk to someone who understands agentic security operations

Have a direct conversation about your environment with a member of our team.
How AI-led investigation reduces analyst workload
Where automation runs, where human judgement takes over, and how that split is governed in practice.
What this looks like inside your Microsoft stack
Specific to Defender, Sentinel, and Entra
Whether your environment is ready
An honest assessment of what is needed to operationalise agentic response across your current setup.
VISIONX AND MICROSOFT FAQS

Common Questions We Get Asked

What Microsoft products does VisionX support?

VisionX connects natively across the full Microsoft security stack. This includes Microsoft Defender for Endpoint, Defender for Identity, Defender for Office 365, Defender for Cloud Apps, Microsoft Sentinel, and Azure infrastructure. Every signal across endpoint, identity, email, cloud and network feeds into a single detection and response engine, so threats cannot move between tools undetected.

Do we need to replace our existing Microsoft licences or tools?

No. VisionX works within your existing Microsoft environment. If you are running E3 or E5 licences, VisionX activates the security capabilities you are already paying for but not fully operationalising. There is no agent sprawl, no third-party log forwarders, and no additional attack surface introduced. We work inside your existing governance and compliance posture, not around it.

How quickly can VisionX be deployed?

Most organisations are live within 5 to 10 days. Because VisionX connects via Microsoft native APIs, there is no rip and replace and no lengthy procurement process. Onboarding includes full environment baselining, custom detection rule configuration and analyst familiarisation with your specific environment before monitoring begins.

What does complete response mean in practice?

It means our analysts do not stop at the alert. When a threat is confirmed, VisionX triggers pre-approved SOAR playbooks that act immediately — isolating hosts via Defender for Endpoint, revoking Entra ID sessions, blocking malicious IPs, and purging malicious emails — all without waiting for manual approval. Every action is logged, reversible and reported. You get a full post-incident report within four hours. Most vendors hand the response back to your internal team. We close it.

How does VisionX support our compliance obligations?

Every incident generates a structured report mapped to MITRE ATT&CK, with full audit trails for NIS2, DORA, ISO 27001, Cyber Essentials and GDPR. Your board and auditors get the evidence they need without additional effort from your team. For organisations under NIS2, VisionX supports the 24h early warning and 72h incident reporting timelines directly, with SOC analysts who understand the regulatory context, not just the technical one.

We already have an internal security team, is VisionX still a fit?

Yes, and most of our clients do. VisionX is designed to extend your internal team, not replace it. Your team retains full visibility and control. What changes is the operational burden — monitoring, triage, investigation and containment are handled by our analysts around the clock, freeing your internal team to focus on security strategy, architecture and the work that actually requires their expertise. Most clients find their team becomes more effective, not redundant.