Assess, Track and Visualise Cybersecurity Risk in One Place

Peer Review

Gartner brand name text logo in white with registered trademark symbol.
5-star rating
4.8

Proven Trust

Dark blue circle with two overlapping checkmarks, one green and one light blue.
ISO 27001 text with a globe outline symbol on a black background.
2025 winner badge for Cyber Security Excellence Awards with gold and black design.

Risk Hub is a dedicated feature set in VisionX that streamlines risk management. It brings maturity assessments, a risk register, and risk visualisations together, so you can see your risk, act on it, and improve your overall security posture.

Talk to our team

319% ROI

Independent ROI Study

<6 Months

Payback

€2M

Net Present Value
By now, most organisations have already
suffered significant business impact.
RISK HUB CAPABILITIES

What Risk Hub Does

Risk Hub brings assessment, tracking, and visualisation into one feature set, so cybersecurity risk is something you manage continuously, not something you rebuild for every audit.
Maturity assessments
Know where you stand on NIST CSF 2.0 across all six functions: Govern, Identify, Protect, Detect, Respond, and Recover.
Why it matters
Benchmarking against NIST targets shows your gaps and gives you clear, audit-ready evidence of cybersecurity due diligence.
Risk register
Every risk lives in one register, whether it's entered by hand or generated from Jira, SIEM, assessments, NoPhish, or KnowBe4.
Why it matters
Automated generation and integrations cut manual effort and keep your record accurate as new risks emerge.
Risk visualisations
Maturity and register data combine into one view of progress, priority, and mitigation.
Why it matters
Radar, historical, distribution, trend, response, and status views turn risk data into decisions you can act on.
MATURITY ASSESSMENTS

Know Exactly How Mature Your Security Is

The Information Security Maturity Assessments feature is a comprehensive tool to help you evaluate and enhance cybersecurity maturity. It is built on the latest NIST Cybersecurity Framework (CSF) 2.0, developed by the National Institute of Standards and Technology, to strengthen resilience across six core functions.
GV Govern
ID Identity
PR Protect
DE Detect
RS Respond
RC Recover
RISK DATA VISUALISATIONS

See Your Risk Landscape at a Glance

The Risk Data Visualisations feature gives a clear, visual overview of cybersecurity risks and trends. It combines data from both Maturity Assessments and the Risk Register, so you can assess, prioritise, and track your risk landscape with ease.
Goal
Visual
What it shows
Unified risk overview
VisionX
Maturity and register data combined
A comprehensive view of risk from both sources.
Track maturity progress
VisionX
Radar chart, historical chart
Improvement in cybersecurity maturity over time.
Prioritise risks
VisionX
Risk distribution, trend over time
Which high-impact risks need attention first.
Monitor risk mitigation
VisionX
Risks by response, risks by status
How risk resolution efforts are progressing.
RISK REGISTER

One Register for Every Risk You Track

The Risk Register is a comprehensive tool for documenting, tracking, and managing cybersecurity risks across categories. It is a centralised repository where risks can be categorised, visualised, and analysed for better decisions. By integrating with other systems, it streamlines risk management and gives real-time insight into your risk landscape.

Efficient risk documentation

Create and manage a wide range of risks, from manual entries to automated imports from integrated systems.

Automated risk generation

Generate risks automatically from sources like Jira, SIEM, Maturity Assessments, NoPhish, and KnowBe4, reducing manual effort and keeping records accurate.

Scalable and centralised repository

Maintain a comprehensive register that scales, documenting and tracking risks as they emerge so your approach stays consistent across the organisation.

Integration and automation

Seamless connections with your systems enable automated updates, improving the efficiency and accuracy of risk management.
SentinelOne company logo with stylized shield icon to the left of the text.
EXPLORE THE MODULES INSIDE VISIONX

Your risk, and the Stack Behind it

VisionX Application

Maturity assessments, a living risk register, and human-written recommendations, so governance is something you monitor, not something you scramble for once a year.
Maturity assessments
Risk register
Benchmark advisor

Technology Integrations

Keep the tools you've already invested in. VisionX runs on top of your SIEM, EDR, and XDR platforms and gives you one view across all of them.
Microsoft
Crowdstrike
SentinelOne
Splunk

Take the Details With You

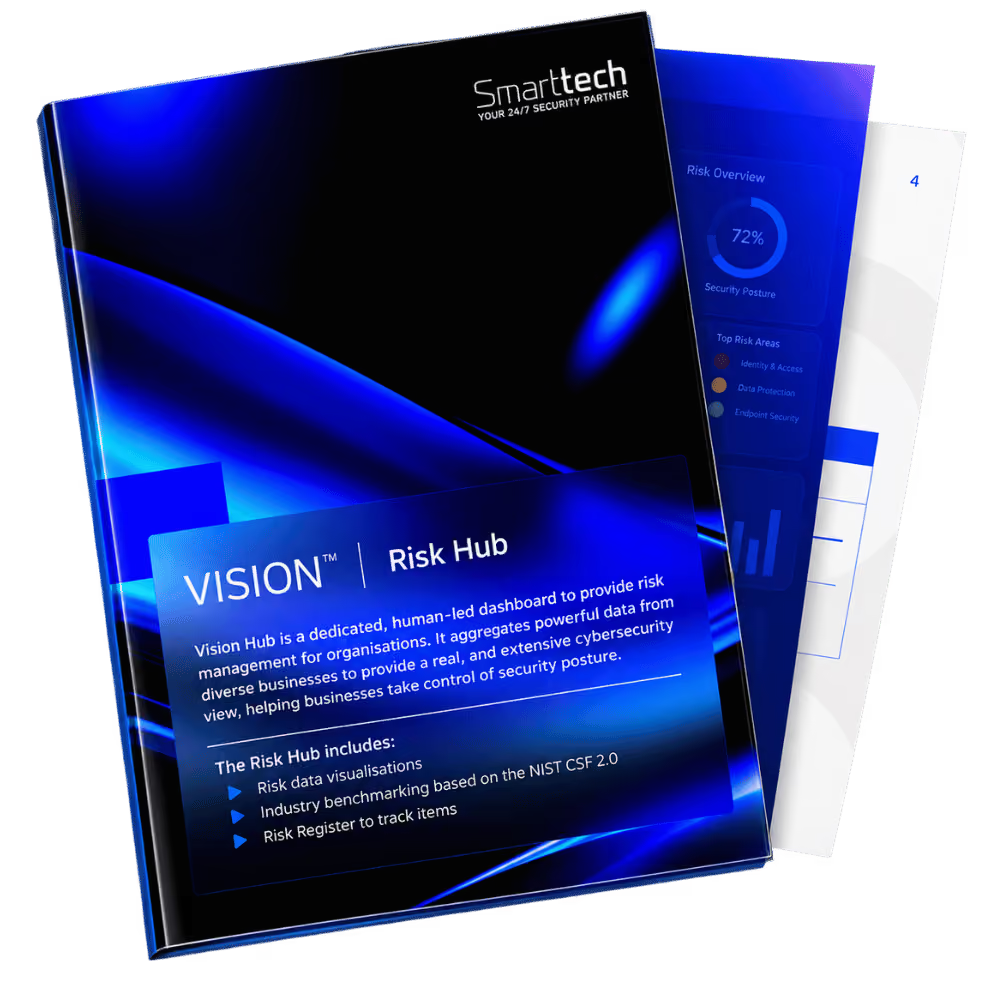
Download the VisionX Risk Hub guide for a full walkthrough of maturity assessments, the risk register, and the visualisations.
VISIONX FAQs

Common Questions We Get Asked

Is the 319% ROI figure something we can expect too from VisionX?

It's what Forrester modelled for one customer's environment and deployment scale, not a guarantee. Your result depends on your current tooling, headcount, and incident history. We're happy to build a tailored estimate using the same framework.

Does the AI make decisions on its own within VisionX?

No. AI drafts the summary and queues the response, but a Smarttech247 analyst reviews and approves every report and every action before anything reaches you or runs against your environment. You get the speed of automation with a human still accountable for the call.

Can we keep our current SIEM or EDR with VisionX?

Yes. VisionX is technology-agnostic by design. We integrate with your existing SIEM, EDR, or XDR platform for faster onboarding and to protect the investment you've already made. There's no need to rip and replace unless you want to.

What makes VisionX different from other MDR platforms?

VisionX is built proactive and intelligence-led, not just alert triage. We combine advanced detection, automated response, and human-led analysis, backed by 24/7 SOC operations. What sets us apart is how deeply we integrate into your existing stack, the real-time visibility we give you, and threat intelligence that's tailored to your business context.

We already have an internal security team, is VisionX still a fit?

Yes, and most of our clients do. VisionX is designed to extend your internal team, not replace it. Your team retains full visibility and control. What changes is the operational burden — monitoring, triage, investigation and containment are handled by our analysts around the clock, freeing your internal team to focus on security strategy, architecture and the work that actually requires their expertise. Most clients find their team becomes more effective, not redundant.

How does VisionX support our compliance obligations?

Every incident generates a structured report mapped to MITRE ATT&CK, with full audit trails for NIS2, DORA, ISO 27001, Cyber Essentials and GDPR. Your board and auditors get the evidence they need without additional effort from your team. For organisations under NIS2, VisionX supports the 24h early warning and 72h incident reporting timelines directly, with SOC analysts who understand the regulatory context, not just the technical one.

How quickly can VisionX be deployed?

Most organisations are live within 5 to 10 days. Because VisionX connects via Microsoft native APIs, there is no rip and replace and no lengthy procurement process. Onboarding includes full environment baselining, custom detection rule configuration and analyst familiarisation with your specific environment before monitoring begins.