Security Tools Shout. VisionX Gives You One Clear Answer

Peer Review

Gartner brand name text logo in white with registered trademark symbol.
5-star rating
4.8

Proven Trust

Dark blue circle with two overlapping checkmarks, one green and one light blue.
ISO 27001 text with a globe outline symbol on a black background.
2025 winner badge for Cyber Security Excellence Awards with gold and black design.

Start the day knowing your okay. VisionX turns noise into one clear, role-aware answer across your SIEM, EDR, identity, network, cloud and OT, so your team knows exactly where it stands, not hunting across five different consoles to find out.

Talk to our team

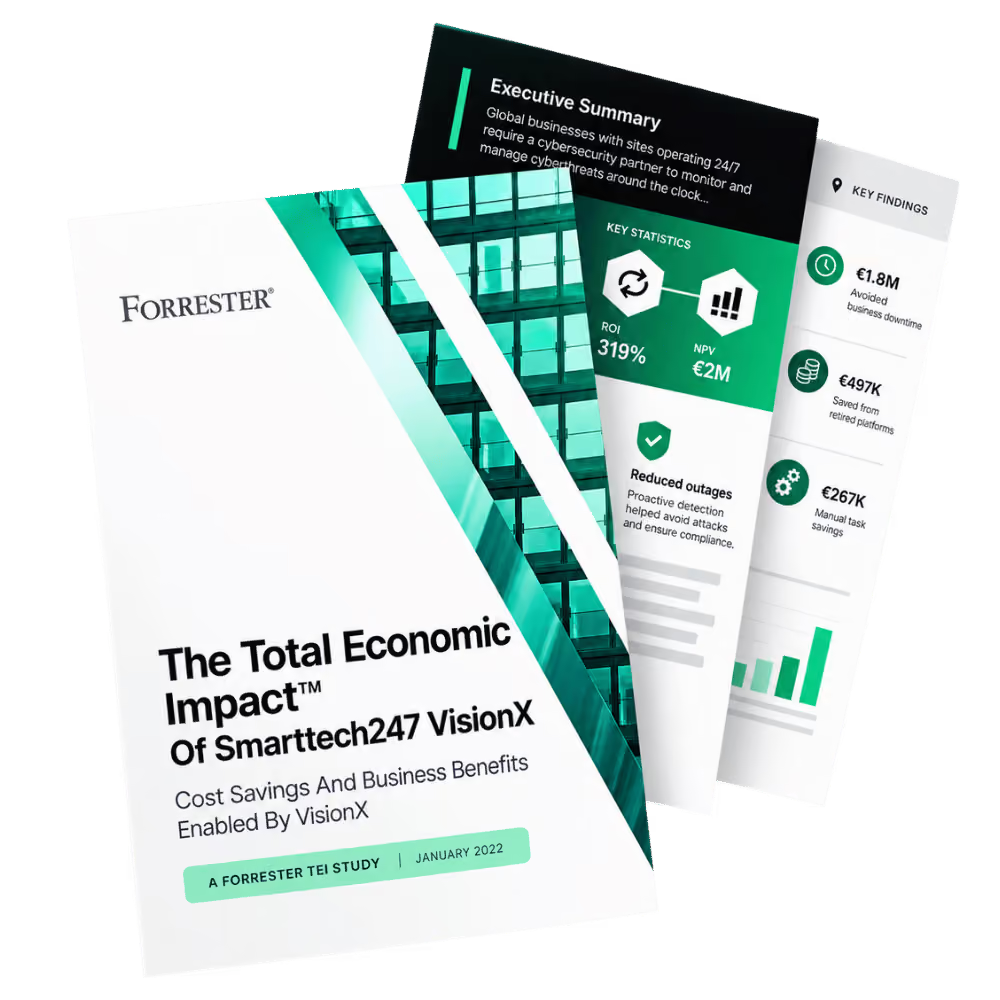
319% ROI

Independent ROI Study

<6 Months

Payback

€2M

Net Present Value
By now, most organisations have already
suffered significant business impact.
A SINGLE PANE OF GLASS INTO YOUR SECURITY OPS

Disconnected Tools are Stealing Your Time

When security tools operate in isolation, your team loses visibility, loses hours, and never quite gets to relax. VisionX brings your whole security ecosystem into one platform, so the question each morning has a simple answer.
Fragmented tooling and data
You can't give the board a straight answer when your risk lives across five different consoles. VisionX pulls telemetry from your SIEM, EDR, network, identity, and cloud into one picture, so you always know where you stand.
Screenshot of VisionX and Google SecOps integrations for cybersecurity.
Slow, manual correlation
Your analysts burn hours stitching alerts together by hand, and by the time they spot the pattern, the attacker's already moved. VisionX correlates activity across every tool the moment it happens, so your team acts on the signal, not the backlog.
Screenshot of VisionX and Google SecOps integrations for cybersecurity.
Blind spots in your stack
The worst conversation you'll ever have starts with "how long had that log source been dead". VisionX watches every connected integration and flags the moment one drops, before it becomes the gap nobody caught.
Screenshot of VisionX and Google SecOps integrations for cybersecurity.
Inconsistent recommendations
An alert with no next step just becomes another item nobody owns. VisionX gives you a human-written recommendation, a priority, and an owner, so remediation doesn't stall waiting on someone to interpret it.
Screenshot of VisionX and Google SecOps integrations for cybersecurity.
No single posture score
Every vendor hands you a different grade, calculated a different way, in a different format. VisionX gives you one posture score across every tool, so you can tell the board the truth in one number.
Screenshot of VisionX and Google SecOps integrations for cybersecurity.
Compliance scramble
Compliance shouldn't turn into a fire drill every time an auditor or a new regulation shows up. VisionX scores your maturity against the frameworks you're actually regulated against, so you walk in with evidence, not a scramble.
Screenshot of VisionX and Google SecOps integrations for cybersecurity.
SentinelOne company logo with stylized shield icon to the left of the text.
BUILT AROUND HOW YOUR TEAM WORKS

VisionX Shows Each Role Exactly What They Need

Your queue, prioritised
You open 10 tabs just to work out which alert is actually a P1. VisionX hands you your queue already prioritised, P1s first, with the context attached, so you act on an incident instead of guessing at an alert.
P1
Lateral movement, HOST-012
P2
Credential theft attempt
P3
Policy violation, flagged
Your team's performance, over time
VisionX tracks triage rates, MTTA and MTTR by priority over time, so you can show leadership your team is handling more scale without more headcount.
ANALYST TIME ON REAL INVESTIGATIONS
62%
illustrative only, not a sourced figure
Your risk posture, over the long term
The board doesn't want to hear about yesterday's incident. It wants to know if you're actually getting safer. VisionX tracks your maturity over time and turns it into board-ready reporting, so you can answer that question with a trend, not a guess.
74
POSTURE SCORE
illustrative trend
exportable as board PDF
AI-POWERED AUTOMATION

Where alerts turn into action

Most tools generate an alert and stop there. VisionX goes further, AI triages the case, drafts the summary, and queues the response, so your analysts spend their time on judgement calls instead of busywork.

A human checks everything first: every AI-drafted report is reviewed and approved by an analyst before it leaves our SOC, and every action is logged end to end.
VIP impersonation detection
Automated email remediation
Full audit trail
01 | DETECTED
An alert comes in
02 | DRAFTED
AI drafts the summary and the response
03 | MANDATORY GATE
An analyst reviews and approves, every time
04 | EXECUTED
The action runs immediately
05 | LOGGED
Every step recorded in the audit trail
EXPLORE THE MODULES INSIDE VISIONX

Your risk, and the Stack Behind it

Risk Hub

Maturity assessments, a living risk register, and human-written recommendations, so governance is something you monitor, not something you scramble for once a year.
Maturity assessments
Risk register
Benchmark advisor

Technology Integrations

Keep the tools you've already invested in. VisionX runs on top of your SIEM, EDR, and XDR platforms and gives you one view across all of them.
Microsoft
Crowdstrike
SentinelOne
Splunk
VISIONX COVERAGE

What You Gain Traditional Platforms Can't Deliver

Capability
VisionX
Traditional Providers
Stack coverage
VisionX
Tech-agnostic across SIEM, EDR, identity, network, cloud, and OT
Traditional MDR
Tied to one vendor or a narrow tool set
Role-aware views
VisionX
Dedicated views for analysts, managers, and CISOs, with the right context for each
Traditional MDR
One generic queue for everyone
Incidents and SLAs
VisionX
Live timelines, owners, next actions, MTTA, and MTTR tracked by default
Traditional MDR
Ticket lists with limited SLA visibility
Log-source coverage
VisionX
Health and completeness of every data source, surfaced in real time
Traditional MDR
Blind spots discovered after an incident
Risk and CISO Hub
VisionX
Dedicated, white-glove, built around your programme
Traditional MDR
Standardised and generic, not tailored
User risk loop
VisionX
Maturity assessments, risk register, recommendations, and benchmarks in one place
Traditional MDR
Spreadsheets and slide decks outside the platform
Partnership approach
VisionX
People-led, built around your outcomes
Traditional MDR
Reactive, and faceless
Featured manufacturing case study
Global Metal Packaging Manufacturing

Trivium Packaging Case Study

7, 200

Employees

57

Locations globally

50

Manufacturing plants
Roel Schouten
Vice President Information Security
"If they discover a high-confidence attack at 3 o'clock in the night, they can isolate the system, no matter how critical the system is. I don't have 24/7 coverage in my team. It's good to have someone there that we know is helping us around the clock."

Customer Challenges

Trivium Packaging manufactures cans and aerosols across 57 locations and roughly 50 plants globally. The business runs on uptime, and ransomware groups know it: disrupt output, extract a ransom. Trivium learned this in 2021 after an enterprise-wide ransomware attack.

Trivium's internal security team is lean, around 10 people, spread across Europe and the US, with no way to sustain 24/7 coverage on their own. An attack at 3am doesn't wait for business hours.

Customer Challenges

Smarttech247 gives Trivium round-the-clock coverage its own team can't sustain, with authority to isolate a compromised system the moment a high-confidence attack is detected, no approval call required.

The Results

0

Critical incidents

1,401

Threats caught

80%+

More phishing reports,
‍zero drop in accuracy
VISIONX PRODUCT GUIDES

Get More Details Behind VisionX

Three guides, one for Microsoft-specific SOC automation, one for core MDR, one for Risk Hub. Download the one that matches what you're actually evaluating.

VisionX Risk Hub Product Guide

VisionX Risk Hub gives organisations one place to assess, track and visualise cybersecurity risk, built on NIST CSF 2.0 maturity benchmarking.

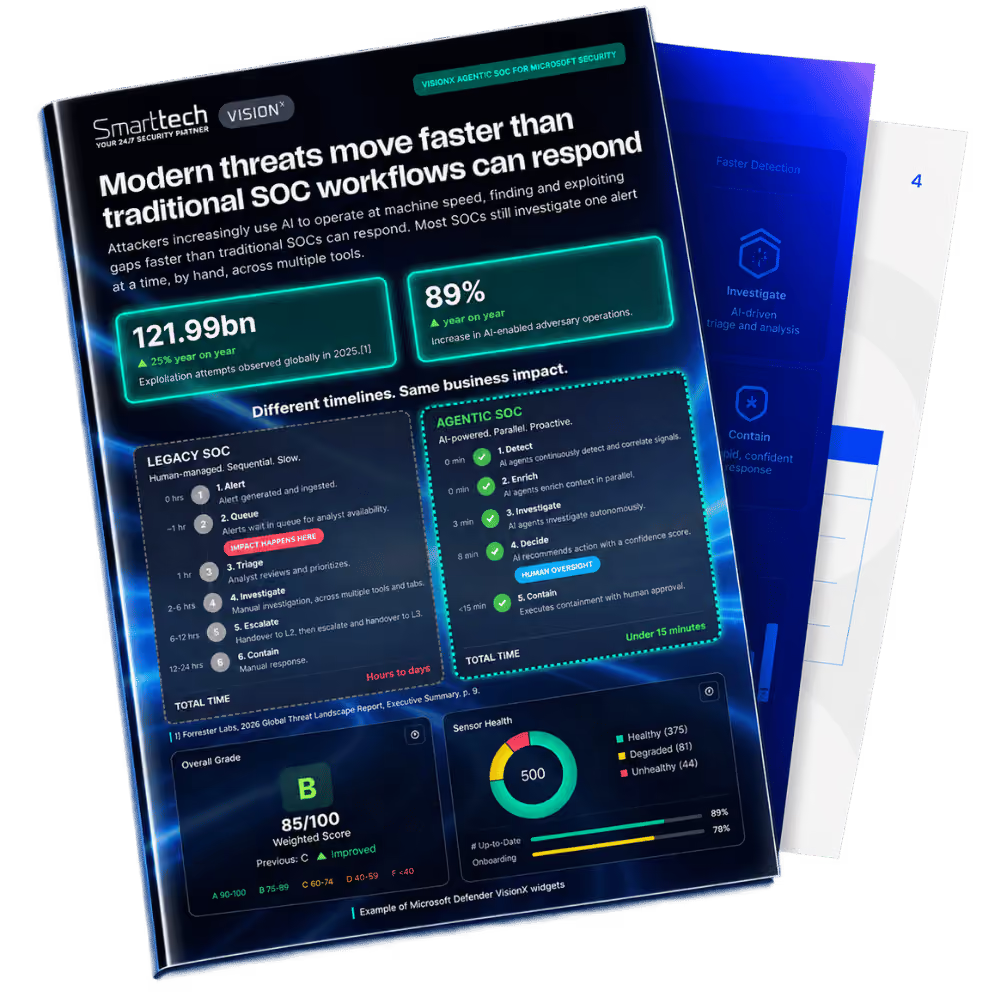
VisionX Agentic SOC for Microsoft Security

Transform Microsoft security operations with VisionX Agentic SOC. Automate triage and investigation, target sub-15-minute response, and retain human oversight for critical actions.

VisionX MDR Product Guide

VisionX MDR delivers 319% ROI in under 6 months and 50% risk reduction in the first 180 days, with active defence in under 15 minutes.

Why the Organisation Chose Smarttech247

The manufacturer had grown through acquisition, leaving fragmented security tooling and no incident response process in place. VisionX consolidated this into 24/7 monitored coverage, deployed country-by-country starting with a two-week rollout to the first site.

  • Detected the WannaCry ransomware incident early, before it caused damage
  • Replaced ad hoc security checks with continuous monitoring
  • Gave board-level visibility into risk posture for budget decisions
VISIONX FAQs

Common Questions We Get Asked

Is the 319% ROI figure something we can expect too from VisionX?

It's what Forrester modelled for one customer's environment and deployment scale, not a guarantee. Your result depends on your current tooling, headcount, and incident history. We're happy to build a tailored estimate using the same framework.

Does the AI make decisions on its own within VisionX?

No. AI drafts the summary and queues the response, but a Smarttech247 analyst reviews and approves every report and every action before anything reaches you or runs against your environment. You get the speed of automation with a human still accountable for the call.

Can we keep our current SIEM or EDR with VisionX?

Yes. VisionX is technology-agnostic by design. We integrate with your existing SIEM, EDR, or XDR platform for faster onboarding and to protect the investment you've already made. There's no need to rip and replace unless you want to.

What makes VisionX different from other MDR platforms?

VisionX is built proactive and intelligence-led, not just alert triage. We combine advanced detection, automated response, and human-led analysis, backed by 24/7 SOC operations. What sets us apart is how deeply we integrate into your existing stack, the real-time visibility we give you, and threat intelligence that's tailored to your business context.

We already have an internal security team, is VisionX still a fit?

Yes, and most of our clients do. VisionX is designed to extend your internal team, not replace it. Your team retains full visibility and control. What changes is the operational burden — monitoring, triage, investigation and containment are handled by our analysts around the clock, freeing your internal team to focus on security strategy, architecture and the work that actually requires their expertise. Most clients find their team becomes more effective, not redundant.

How does VisionX support our compliance obligations?

Every incident generates a structured report mapped to MITRE ATT&CK, with full audit trails for NIS2, DORA, ISO 27001, Cyber Essentials and GDPR. Your board and auditors get the evidence they need without additional effort from your team. For organisations under NIS2, VisionX supports the 24h early warning and 72h incident reporting timelines directly, with SOC analysts who understand the regulatory context, not just the technical one.

How quickly can VisionX be deployed?

Most organisations are live within 5 to 10 days. Because VisionX connects via Microsoft native APIs, there is no rip and replace and no lengthy procurement process. Onboarding includes full environment baselining, custom detection rule configuration and analyst familiarisation with your specific environment before monitoring begins.