Empower Your Security With VisionX Managed Detection & Response

Give your organisation 24/7 monitoring, real-time threat intelligence, precision detection engineering, proactive threat hunting, and full incident response in one integrated service built to stop attacks fast.

Peer Review

Gartner brand name text logo in white with registered trademark symbol.
5-star rating
4.8

Proven Trust

Dark blue circle with two overlapping checkmarks, one green and one light blue.
ISO 27001 text with a globe outline symbol on a black background.
2025 winner badge for Cyber Security Excellence Awards with gold and black design.

Trusted by clients worldwide

Logo
Logo
Logo
Logo
Logo
Logo

Why Most Organisations Struggle with Managed Detection and Response

Most organisations face the same core challenges when it comes to MDR: too many threats to keep up with, gaps in specialist expertise, and slow or uncertain response when incidents occur.

Overwhelming Threat Volume

Security teams can’t keep up with constant alerts, false positives, new attack vectors, and evolving threats.

Gaps In Expertise & Coverage

Even well-resourced teams struggle to recruit and retain specialists in detection engineering, threat hunting, deep investigation, and incident response.

Slow Incident Response

When something suspicious happens, most organisations lack clear playbooks, rapid investigation capability, and the forensic depth needed to act decisively.

Lack of 24/7 Coverage

Most teams can’t maintain round-the-clock vigilance. Limited coverage creates blind spots overnight, allowing threats to go undetected when response time matters most.

Image

How Smarttech247 Delivers Managed Detection and Response

Collect & enrich

Telemetry from SIEM, EDR, identity, network, cloud, SaaS, and OT is aggregated and enriched with multiple threat intelligence feeds.

Detect & prioritise

Detection engineering turns raw data into high-fidelity rules and use cases; 24/7 analysts focus on offences that actually matter.

Investigate & respond

L1–L3 analysts correlate activity across systems, contain threats (where authorised), and coordinate remediation.

Learn & harden

Findings feed into threat hunting, new detections, and remediation & forensics so the same path can’t be used twice.
Tech Agnostic

You Bring the tech.
We do the hard work.

Connect your tools, connect your teams. We link to SIEMs you use, and integrate them with VisionX. We will always be tech agnostic.
Integration iconIntegration iconIntegration iconIntegration iconIntegration iconIntegration iconIntegration iconIntegration icon

Everything You Need for a Stronger
Managed Detection and Response Program

A strong MDR programme works only when every part supports your team and strengthens your security. These connected capabilities come together to give you clearer visibility and faster action when it matters.

Managed Detection & Response

VisionX gives Level 1 and Level 2 teams a unified view of incidents, risk, coverage and automation so they can triage faster, investigate deeper and act with clarity.

Learn more

Arrow Icon
Offensive Security

Intelligence that anticipates attacker behaviour and enriches every alert. It gives analysts context, reduces noise and helps you stay ahead of emerging threats.

Learn more

Arrow Icon
Information Security

Continuous tuning of detections to reduce false positives and sharpen accuracy. Your ruleset improves over time instead of degrading as the environment changes.

Learn more

Arrow Icon
VisionX Platform

 Root-cause analysis and clear recovery steps after an incident. You get stronger controls, safer systems and lessons that prevent repeat events.

Learn more

Arrow Icon
MDR for Identity

Proactive monitoring for leaked data, credentials and early signs of compromise. It alerts you to risk before attackers attempt to use it.

Learn more

Arrow Icon
MDR for Cloud

Fast containment, coordinated action and forensic support when incidents strike. The team moves quickly to limit impact and guide recovery.

Learn more

Arrow Icon
MDR for OT

Named analysts watch over your environment day and night. You get real human decision-making, rapid escalation and decisive action at any hour.

Learn more

Arrow Icon
Expertise by Vertical

Targeted hunts that uncover stealthy threats your tools may miss. This reduces dwell time and strengthens your visibility across the environment.

Learn more

Arrow Icon
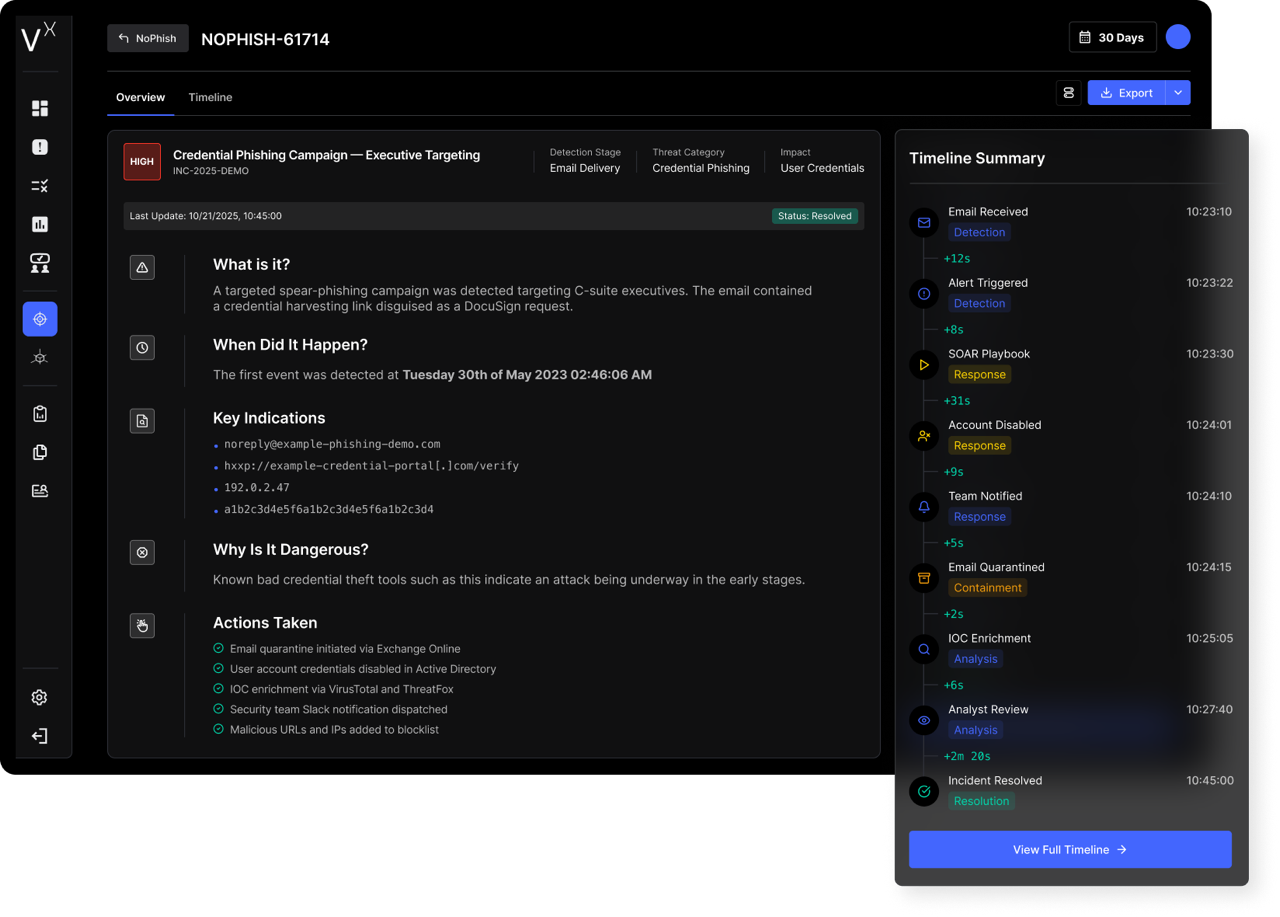
Dashboard mockup

VisionX for Managed Detection and Response

VisionX is your transparent hub for MDR — tech-agnostic and built to work with Microsoft Sentinel, Splunk, QRadar, leading EDRs, and major cloud/SaaS platforms.

Real-time incidents & SLAs

See live timelines, owners, next actions, and SLA status so nothing stalls.

Log-source coverage

Know exactly which data sources are connected, healthy, or missing, with prioritised fixes.

Risk Hub

Link incidents and exposure to business risk, track resilience metrics, and assign owners and due dates.

NIST assessments and CISO Hub

Run NIST CSF 2.0 baselines, map to ISO 27001, and use executive dashboards with exportable, audit-ready reports.

AI Assistant

Ask plain English questions about incidents, risks, or coverage and get contextual answers from your own data.

Automation (SOAR)

Execute preapproved playbooks to isolate endpoints, block domains and IPs, reset credentials, and enrich cases automatically.

How We Support Organisations Like Yours

Our clients rely on us for consistent, responsive support and clear communication when it matters most.
Their feedback reflects the confidence and stability they gain from working with our team.

"Smarttech247 gave us confidence fast. We were live on VisionX within weeks and the partnership has only strengthened since."

CTO

FBD Insurance

"Smarttech247 gives us more than a security operations centre. They’ve become a true partner: Responsive, proactive, and focused on the details that matter."

CISO

Autonation

"What makes Smarttech247 different is their people. Skills can be taught, but genuine commitment can’t: they’re proactive, they listen, and they understand what matters to us."

Information Security Manager

Clunetech

What You Gain That Traditional
Managed Detection and Response Can’t Deliver

Traditional MDR often struggles with limited visibility, slow investigations, and rigid processes that can’t
keep up with modern threats. We close those gaps with faster response, clearer context, and capabilities
that adapt to your organisation’s needs.
Feature / Capability
Smarttech247 MDR
Traditional MDR Providers
Effective Threat Detection
Expert Detection Engineering Customised to your Environment
Basic generic detection & alerting
Incident Response
Understand and Deliver against your Imperatives.
You get an alert
Managed Data Security and Phishing
Holistic and Multi-layer
Focus on endpoints and networks.
Visibility into your security operations
Powered by VisionX you have Complete Transparency
Services are opaque and reactive
Customer Service
Dedicated, White Glove
Standardised and vanilla – not tailored
Integration and Flexibility
Risk Aware! We Maximise Monitoring Coverage!
Limited, custom costs
Partnership Approach
People Led, We put your outcomes first!
Reactive, Faceless
Support

Everything You Need to Know Before You Decide

Here you’ll find clear answers to the most common questions we hear from security and IT teams. If you need anything more specific, we’re always here to help.
What makes VisionX different from other MDR vendors?
VisionX is designed with a proactive, intelligence-led approach that goes beyond traditional alert triage. We combine advanced threat detection, automated response, and human-led analysis — all backed by 24/7 SOC operations. What truly sets us apart is our ability to integrate deeply into your existing tech stack, provide real-time visibility, and deliver tailored threat intelligence aligned to your business context.
Can we keep our current SIEM or EDR?
Yes — VisionX is built to be technology-agnostic and flexible. We integrate seamlessly with your existing SIEM, EDR, or XDR platforms, enabling faster onboarding and maximising your current investments. There’s no need to rip and replace unless you want to.
How fast can we go live?
We can typically have customers live in as little as 5 to 10 business days, depending on the complexity of your environment and existing integrations. Our onboarding process is streamlined, guided by dedicated deployment specialists to ensure a smooth and rapid transition.
Do you offer support outside working hours?
Absolutely. Our Security Operations Centre (SOC) is staffed 24/7/365, providing continuous monitoring, threat detection, and incident response - even on weekends and holidays. Threats don’t work 9–5, and neither do we.
What does your reporting include?
VisionX provides comprehensive, easy-to-understand reporting that includes: Detected threats and their severity, response actions taken, dwell time and resolution metrics, threat trends and recurring attack patterns, executive-level summaries and technical deep dives. We also offer customisable reporting tailored to your industry, regulatory requirements, or board-level needs.

Explore More MDR Services

24/7 SOC Monitoring

Always-on monitoring, triage, response.

Learn more

Arrow Icon

Incident Response

Rapid containment & recovery.

Learn more

Arrow Icon

Detection Engineering

Early warnings on leaked credentials.

Learn more

Arrow Icon

Threat Intelligence

Sharper detections, fewer false positives.

Learn more

Arrow Icon

Threat Hunting

Hypothesis-led hunts, rapid response.

Learn more

Arrow Icon

Remediation & Forensics

Evidence-led recovery, hardening that lasts.

Learn more

Arrow Icon

Ready to scale your security and compliance operations?

We protect your on-premise/cloud/OT environments - 24x7x365

Managed Detection and Response with Complete Visibility

Peer Review

Gartner brand name text logo in white with registered trademark symbol.
5-star rating
4.8

Proven Trust

Dark blue circle with two overlapping checkmarks, one green and one light blue.
ISO 27001 text with a globe outline symbol on a black background.
2025 winner badge for Cyber Security Excellence Awards with gold and black design.

Pure-play managed detection and response from a specialist team. Sub-15-minute incident response, and complete visibility without replacing your existing tools.

Get a free analysis

<15 Min

Incident Response

319% ROI

Measured by Forrester

24/7

AI Powered. Human-Led
By now, most organisations have already
suffered significant business impact.
WHY SMARTTECH247

What MDR Looks Like in Practice

Most MDR providers do the same things. These four are the reasons our clients stay and why they came to us in the first place.
You see everything happening in your environment
Every client has live access to their incidents, SLA performance, log source health, and risk posture. Not a monthly summary, not a report on request. The moment something changes, you see it.
We work with your existing tools. No rip and replace
We support Microsoft Sentinel, Splunk, QRadar, CrowdStrike, SentinelOne, Google SecOps, and LogRhythm; including full deployment and ongoing management. If you built it, we can monitor it. If you want to change it, we can help with that too.
We run your entire security programme
Smarttech247 covers all six NIST functions: govern, identify, protect, detect, respond, recover. Delivered as a managed service from a single partner. Every incident, every tuning cycle feeds directly into recommendations that improve your programme over time.
Named people working on your account
You are assigned named analysts across L1, L2, and L3 from day one. A dedicated project manager runs your onboarding and stays through every QBR. Your analysts learn your environment.
INCIDENT RESPONSE TIMES FOR MDR

From Altert to Containment

Most MDR providers alert. We act. Detection engineers tuning your rules, analysts hunting threats your tools never flagged, and a response team that contains incidents in minutes. Every discipline feeds the next.
3:45pm
Potential ransomware threat detected
Suspicious activity identified through continuous monitoring. The incident is immediately prioritised for investigation.
3:49pm
Incident escalated and response activated
Security specialists assess the threat, activate the agreed response plan and notify key stakeholders.
3:54pm
Threat contained to minimise disruption
Immediate containment measures limit further exposure and protect critical business operations.
3:58pm
Ransomware controlled · blast radius: one server
13 min
The incident is contained to a single server, with no further spread identified. Investigation and recovery planning begin.
Incident contained — sub 15 minutes
Rapid response limited the incident's scope. Stakeholders are informed, evidence is preserved and a post-incident review is initiated.
Incident Response

24/7 SOC Monitoring

Always-on triage, investigation, and escalation across your full environment.
Learn more →

Threat Intelligence

Every alert enriched with context before an analyst touches it.
Learn more →

Remediation
and Forensics

Evidence-led recovery and hardening after every incident.
Learn more →

Identity
Security

Continuous monitoring for compromised identity anomalies.
Learn more →

Cloud
Security

Detection and response across AWS, Azure, GCP, and SaaS platforms.
Learn more →

Operational Technology

Purpose-built monitoring for operational technology and industrial control systems.
Learn more →

NoPhish Email Security

Analyst-led triage and response for phishing campaigns targeting your organisation.
Learn more →

Extended MDR and EDR

Lightweight AI-enabled MDR layered on top of your existing EDR and identity stack.
Learn more →
DELLIVERY MODEL AND SERVICE ACTIVATION

Our MDR and SOC Onboarding Timeline

Weeks 1 - 2

Mobilisation &
Assessment

Target: Weeks 1–2
Scope confirmed, stakeholders and access validated, technical discovery complete, and onboarding waves planned.
Approved and confirmed
Weeks 3 - 5

Priority Monitoring Activation

Target: Weeks 3–5
Priority sources connected and validated, core detections enabled, and escalation contacts confirmed.
24/7 monitoring active
Weeks 6 - 10

Expanded
Coverage

Target: Weeks 6-10
Additional sources onboarded, use cases expanded, and initial tuning completed.
Operational coverage
Weeks 11 - 12

Full Transition & Acceptance

Target: Weeks 11-12
Remaining integrations completed, governance activated, and formal acceptance signed off.
Steady-state service
OUR ANALYSTS BEHIND THE SOC

Meet Some of The People Behind Our SOC

Alexandru Sandu | Director of the SOC
Andrei Constantinescu | SOC QA Manager
Alin Curcan | SOC Technical Manager
Miruna Coman | Senior Security Analyst
Andrei Dumitru | SOC IT Admin
Alexandru Neagu | Tier 3 Security Analyst
Nita Catalin Costel | Tier 3 Security Analyst
Alexandru Dragu | SOC Service Delivery Manager
ONBOARDING PROCESS

Kick-off Meeting and Technical Workshop

Kick-off meeting and technical workshop

Days 1 - 2
Smarttech247 owns
Check - Elements Webflow Library - BRIX Templates
Align on scope, timelines, and communication cadence
Check - Elements Webflow Library - BRIX Templates
Walk through architecture and data source inventory
Check - Elements Webflow Library - BRIX Templates
Define notification workflow and escalation paths
Check - Elements Webflow Library - BRIX Templates
Introduce your named project manager and SOC lead
You own
Confirm stakeholders and technical contacts
Provide architecture diagrams and access credentials
Sign off on SOW and communication preferences
Low customer effort

SIEM setup, log feeds, and integrations

Days 3 – 7
Smarttech247 owns
Check - Elements Webflow Library - BRIX Templates
Deploy event processors and SIEM installation (if new)
Check - Elements Webflow Library - BRIX Templates
Connect standard log feeds: servers, firewalls, EDR, VPN, email
Check - Elements Webflow Library - BRIX Templates
Integrate ticketing system (Jira, ServiceNow, or other)
Check - Elements Webflow Library - BRIX Templates
Configure notification and escalation workflows
You own
Provide Azure / cloud permissions for SIEM deployment
Review and approve data connector configurations
Complete custom log feed requirements if applicable
Medium customer effort — technical inputs needed

SOC quality checks, use case review, and fine-tuning

Days 8 - 10
Smarttech247 owns
Check - Elements Webflow Library - BRIX Templates
Run SOC quality checks against ingested log feeds
Check - Elements Webflow Library - BRIX Templates
Review existing use cases and detection rules
Check - Elements Webflow Library - BRIX Templates
Perform initial fine-tuning to reduce false positive rate
Check - Elements Webflow Library - BRIX Templates
Validate all data sources are healthy and complete
You own
Review tuning output with S247 SOC engineer
Flag any environment-specific context or known benign patterns
Guided — configurations under S247 guidance

Final sign-off and 24/7 monitoring begins

Day 11
Smarttech247 owns
Check - Elements Webflow Library - BRIX Templates
Complete final validation and readiness checks
Check - Elements Webflow Library - BRIX Templates
Confirm all SLAs, escalation paths, and playbooks are active
Check - Elements Webflow Library - BRIX Templates
24/7 SOC monitoring goes live
Check - Elements Webflow Library - BRIX Templates
First weekly operational meeting scheduled
You own
Sign off on full live service
Confirm communication preferences for P1/P2 incidents
Low customer effort
24/7 SOC monitoring live — from signed SOW to full coverage in 11 business days

11

Business days
onboarding

< 15 Min

Incident
response

24/7

Coverage from
day 1

Governance, reporting, and continuous improvement

Ongoing
Smarttech247 owns
Check - Elements Webflow Library - BRIX Templates
Weekly operational meetings: open tickets, use case updates, change management
Check - Elements Webflow Library - BRIX Templates
Monthly service assessment reports: incidents, detection changes, log status
Check - Elements Webflow Library - BRIX Templates
Quarterly business reviews: SLA review, threat landscape, strategic planning
You own
Attendence to weekly and monthly meetings
Review and action recommendations from VisionX Risk Hub
Participate in QBR and maturity review sessions
Low customer effort

Weekly

Operational
meetings

Monthly

Service
reports

Quarterly

Business
reviews

If an attacker is in your environment right now, would you know?

Most organisations would not. Managed detection and response exists to close that gap. Talk to a specialist and find out what full coverage actually looks like.
Book a security assessment
BEFORE YOU DECIDE

Common Questions We Hear

Can we keep our existing SIEM and security tools?

Yes. Smarttech247 is tech-agnostic by design and works with the tools you already own. We support Microsoft Sentinel, Splunk, QRadar, CrowdStrike, SentinelOne, Google SecOps, and LogRhythm, including full deployment and ongoing management. There is no rip-and-replace requirement. If you want to migrate to a different platform at any point, we can manage that too.

What happens when a P1 incident fires at 3am?

P1 incidents at Smarttech247 are acknowledged and commenced within 15 minutes, contractually, at any hour. A SOC analyst validates the alert, escalates to L2, and notifies the customer by phone. A bridge call is created and L2 and L3 analysts join within 60 seconds. Where pre-approved playbooks are in place, containment actions including endpoint isolation, IP blocking, and session revocation execute immediately without waiting for manual approval.

How is managed detection and response different from running our own SIEM?

A SIEM ingests and stores data but does not investigate, triage, hunt, respond, or improve over time without dedicated expertise behind it. Managed detection and response adds the detection engineering, L1 through L3 analyst coverage, threat hunting, incident response, and continuous tuning that turns a SIEM investment into a functioning security programme. Most organisations running their own SIEM generate hundreds of alerts daily with no analyst capacity to action them. Smarttech247 delivers all of this through VisionX, a purpose-built MDR platform, with 24/7 coverage from a specialist team.