5 Signs You've Outgrown Your Current SIEM

Peer Review

Gartner brand name text logo in white with registered trademark symbol.
5-star rating
4.8

Proven Trust

Dark blue circle with two overlapping checkmarks, one green and one light blue.
ISO 27001 text with a globe outline symbol on a black background.
2025 winner badge for Cyber Security Excellence Awards with gold and black design.

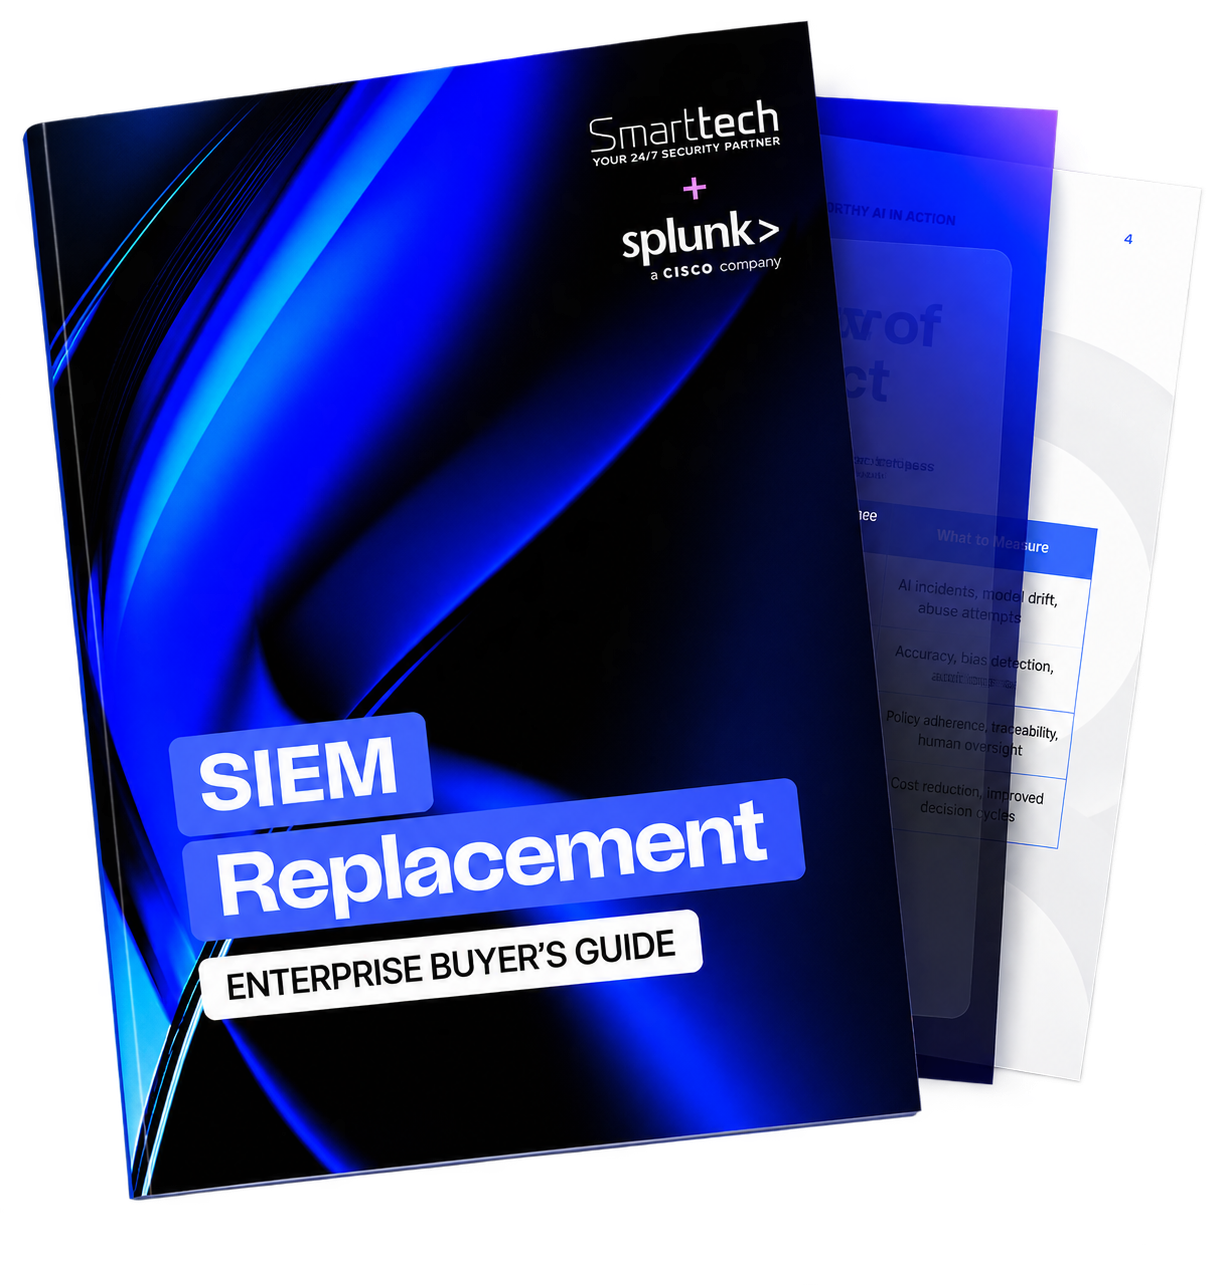
Ingest-based pricing, rigid architectures, and alert noise are driving enterprise teams to reassess their SIEM. This guide gives you a practical starting point, backed by a real migration and Splunk's enterprise platform. Covers:
  • A real-world Splunk migration case study, delivered with zero downtime
  • The 5 signs it's time to move on from your current SIEM
  • A TCO matrix comparing legacy SIEM drain against next-gen Splunk architecture
  • 5 questions to press your current SIEM provider on
  • Splunk's use cases for credential compromise, insider threats, and ransomware detection

Download Your Guide Now

A global manufacturer needed zero downtime, like-for-like functionality on day one, and full team enablement during their Splunk migration. Smarttech247 ran both SIEMs in parallel for two months to validate data integrity before cutover.

  • 6-phase migration framework, from discovery through optimisation and handover
  • Dedicated program management and specialist SIEM engineering
  • Full SOC enablement so your team owns the platform from day one

Who This Guide is For

IT Director / Head of IT

Ingest-based pricing and alert noise are the two most common reasons teams outgrow their SIEM. This kit gives you 5 signs to check for.

CISO / Head of Security

A real migration case study with zero downtime sits inside this kit, alongside Splunk's use cases for credential compromise and insider threats.

Procurement / Vendor Risk Lead

This kit includes a TCO matrix and 5 questions to press your current SIEM provider on before renewal.