Qilin is now the world's busiest ransomware operation

Peer Review

Gartner brand name text logo in white with registered trademark symbol.
5-star rating
4.8

Proven Trust

Dark blue circle with two overlapping checkmarks, one green and one light blue.
ISO 27001 text with a globe outline symbol on a black background.
2025 winner badge for Cyber Security Excellence Awards with gold and black design.

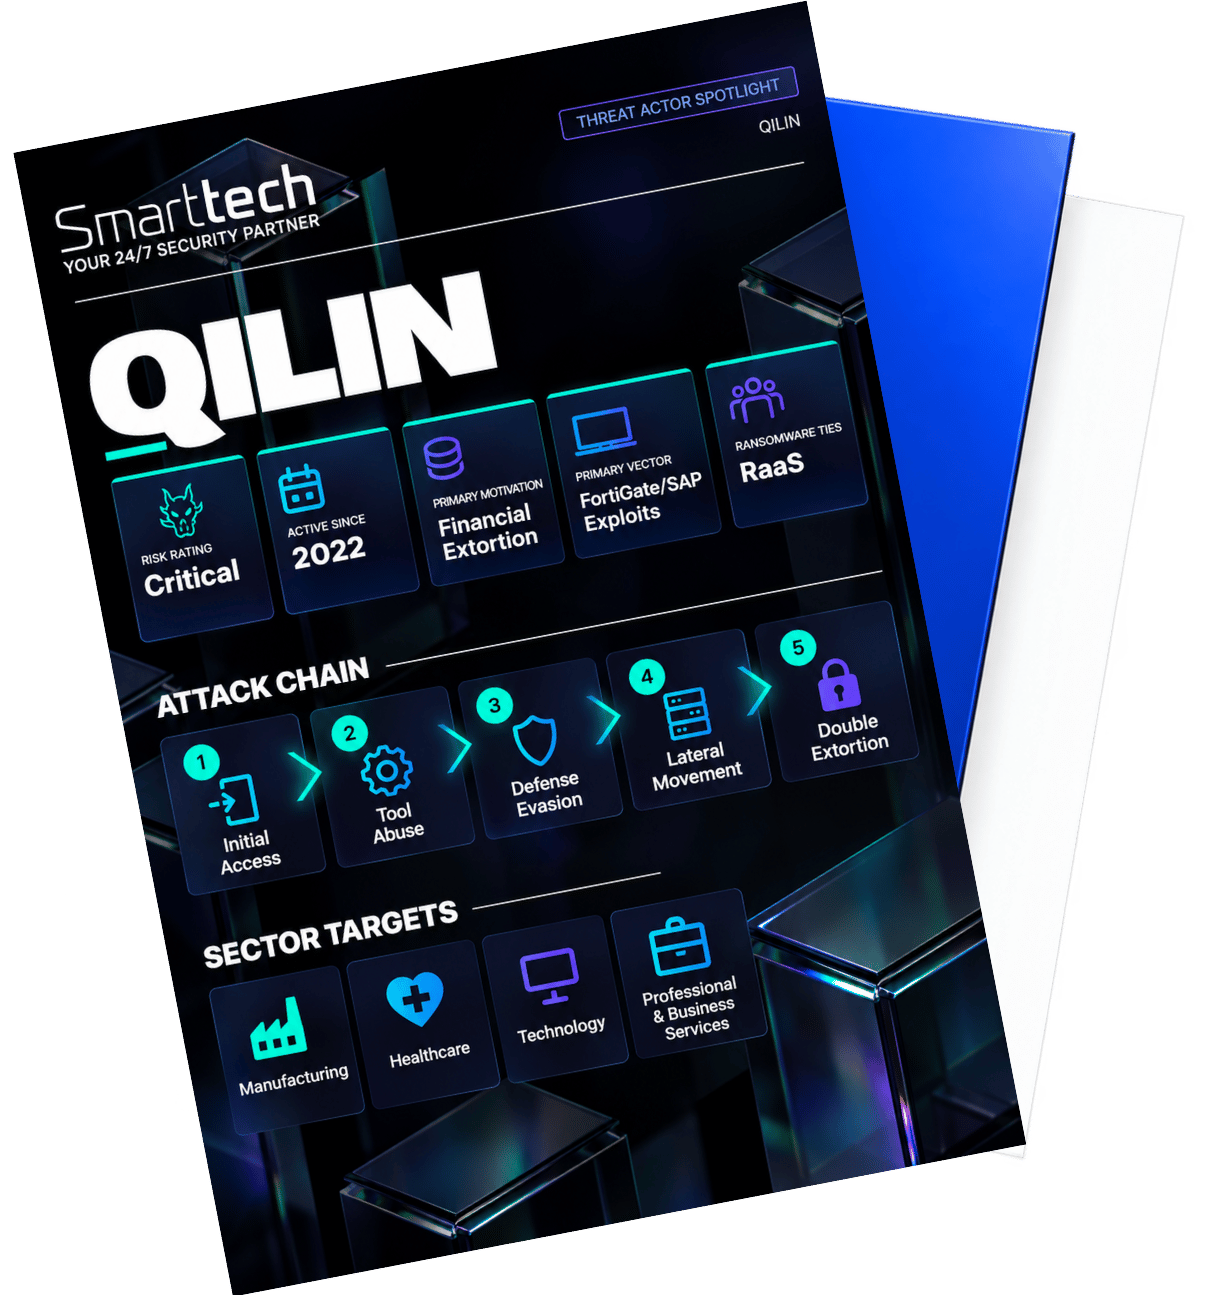
Qilin is now the world's most active ransomware group, with no arrests to date. See how it operates and how to stop it.

Get Guide
It doesn't just encrypt, it negotiates like a law firm

Success here means shutting down the adversary-in-the-middle phishing that gets Qilin in, not negotiating once it's already citing regulatory risk at you.

  • Exploits FortiGate and SAP NetWeaver, or harvests credentials via adversary-in-the-middle phishing
  • Rides legitimate tools like AnyDesk and TeamViewer alongside Cobalt Strike to blend in
  • Frames ransom demands around litigation and regulatory risk in its "call a lawyer" tactic

Who This Guide is For

CISO / Head of Security

No sanctions or arrests mean Qilin has no deterrent but yours. This guide covers the identity hardening that keeps you off its leaderboard.

SOC Manager / Security Operations Lead

Legitimate RMM tools hide Qilin's lateral movement from standard alerts. This guide explains what to watch for across Windows, Linux and ESXi.

IT Director / Head of IT

Exposed edge appliances are the way in. This guide sets out the patching priorities that shut that door before phishing even gets tried.