Handala doesn't want your money, it wants disruption

Peer Review

Gartner brand name text logo in white with registered trademark symbol.
5-star rating
4.8

Proven Trust

Dark blue circle with two overlapping checkmarks, one green and one light blue.
ISO 27001 text with a globe outline symbol on a black background.
2025 winner badge for Cyber Security Excellence Awards with gold and black design.

Handala hijacks cloud admin accounts to wipe devices at scale. See how this Iran-linked group operates and how to stop it.

Get Guide
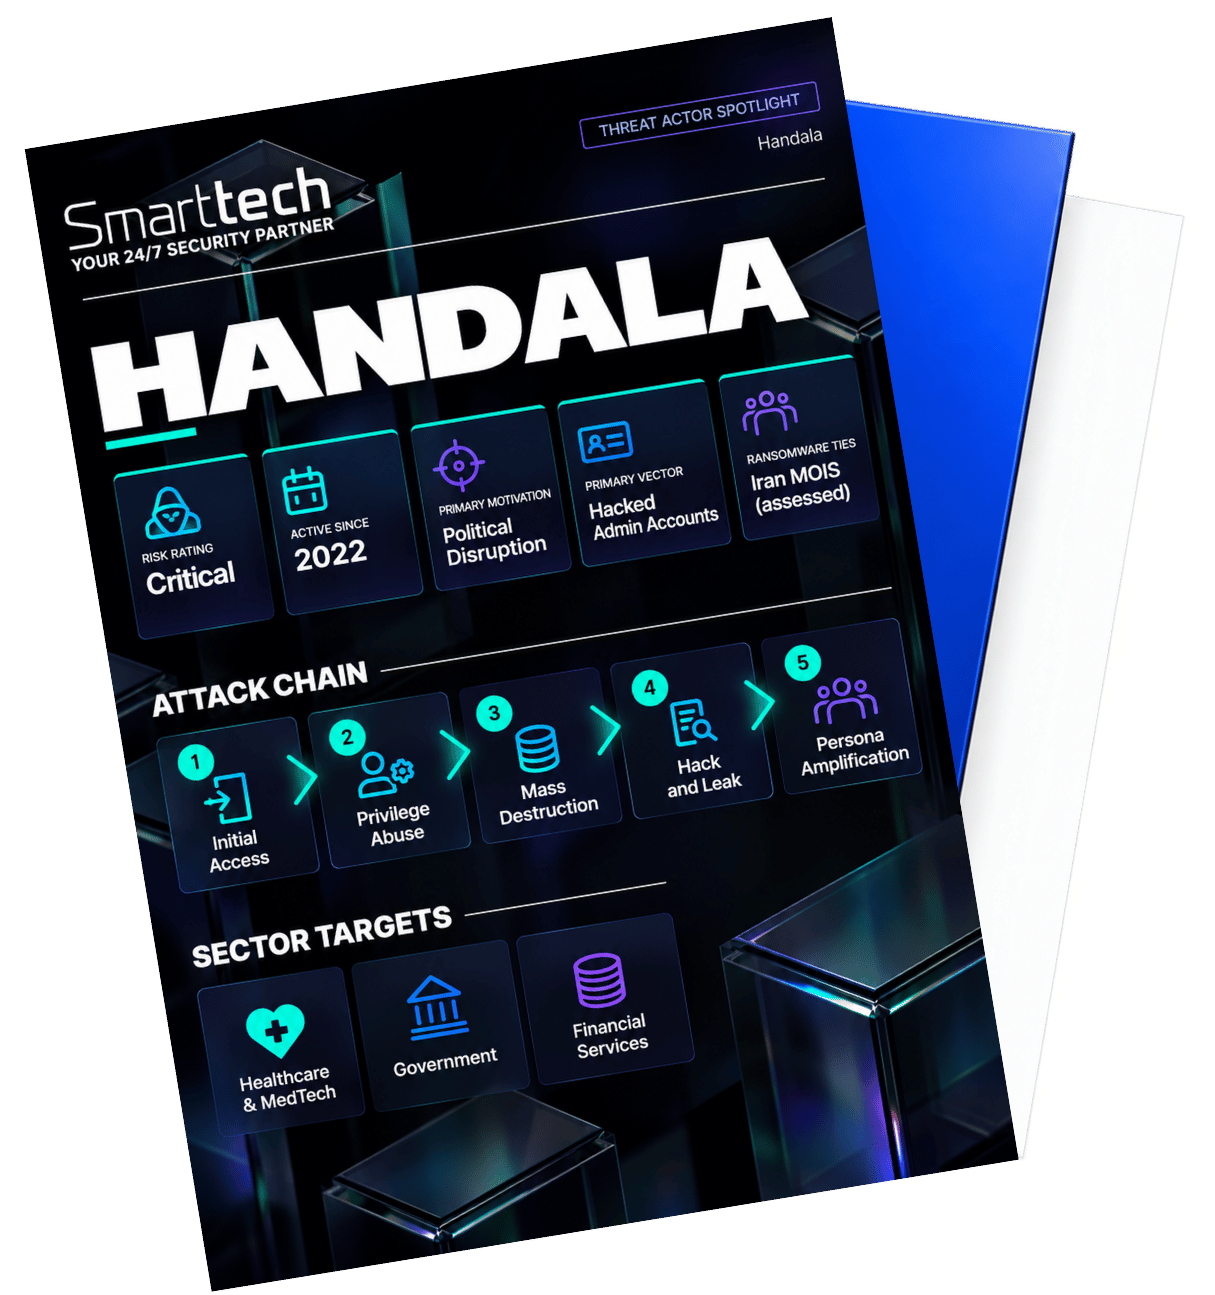
One hijacked admin account, thousands of wiped devices

Success here means containing the Intune or Entra ID admin compromise before a remote-wipe command goes out, not restoring devices after the fact.

  • Phishes or steals credentials to reach Intune or Entra ID Global Admin access
  • Issues legitimate remote-wipe and eSIM-deletion commands, blocking MFA recovery at the same time
  • Amplifies claims via Telegram, X and Tox before independent verification, prioritising publicity over payment

Who This Guide is For

CISO / Head of Security

This is state-linked destruction, not opportunistic crime. This guide covers the privileged access controls that stop a single compromised admin account taking out your fleet.

SOC Manager / Security Operations Lead

Handala uses legitimate MDM commands, not custom malware. This guide explains why standard endpoint detection misses this and what closes the gap.

IT Director / Head of IT

Global Admin access is the whole attack. This guide sets out the segregation and monitoring that keeps that access from being hijacked.