
MDR

Solutions
Partners
About
Resources


FulcrumSec steals data with no malware at all. See how this AI-assisted extortion group operates and how to stop it.
Get Guide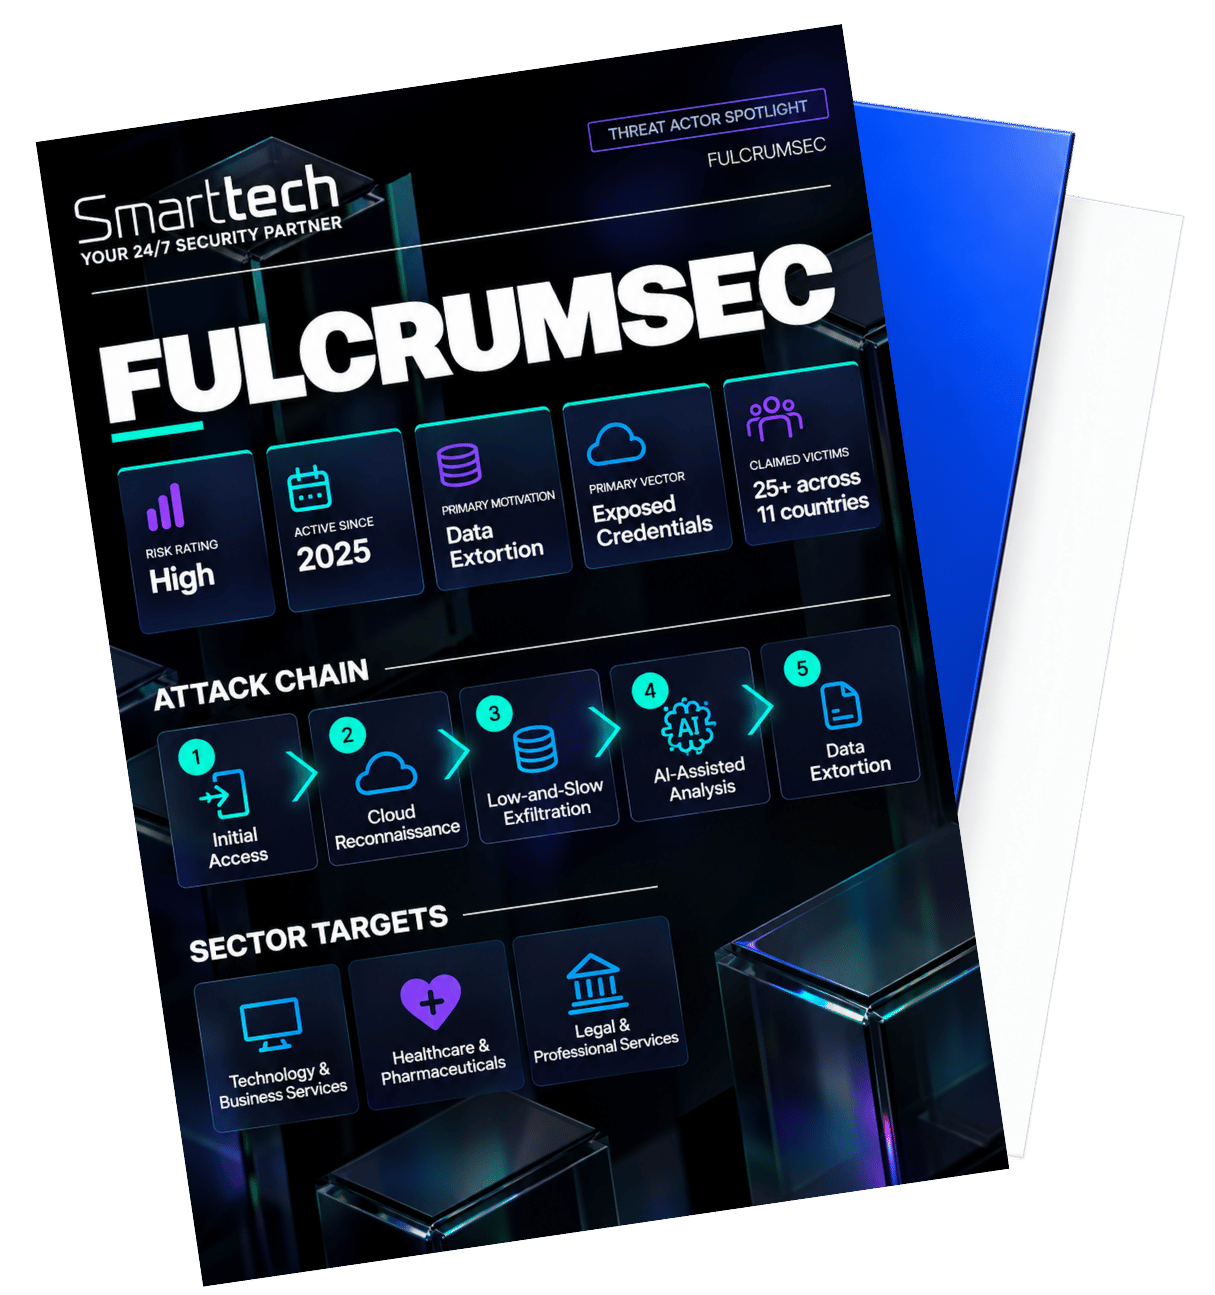
Success here means finding the exposed key before FulcrumSec does, not discovering a leak site posting weeks after quiet exfiltration finished.
A zero-malware model means traditional EDR and antivirus won't see this coming. This guide covers the secrets-management and IAM hygiene that actually stops it.
Low-and-slow exfiltration is built to avoid your alerts. This guide explains what cloud-access monitoring needs to catch instead.
Exposed API keys in code repos are the whole entry point. This guide sets out the credential and token hygiene that closes that gap.