DireWolf deletes your backups before it encrypts

Peer Review

Gartner brand name text logo in white with registered trademark symbol.
5-star rating
4.8

Proven Trust

Dark blue circle with two overlapping checkmarks, one green and one light blue.
ISO 27001 text with a globe outline symbol on a black background.
2025 winner badge for Cyber Security Excellence Awards with gold and black design.

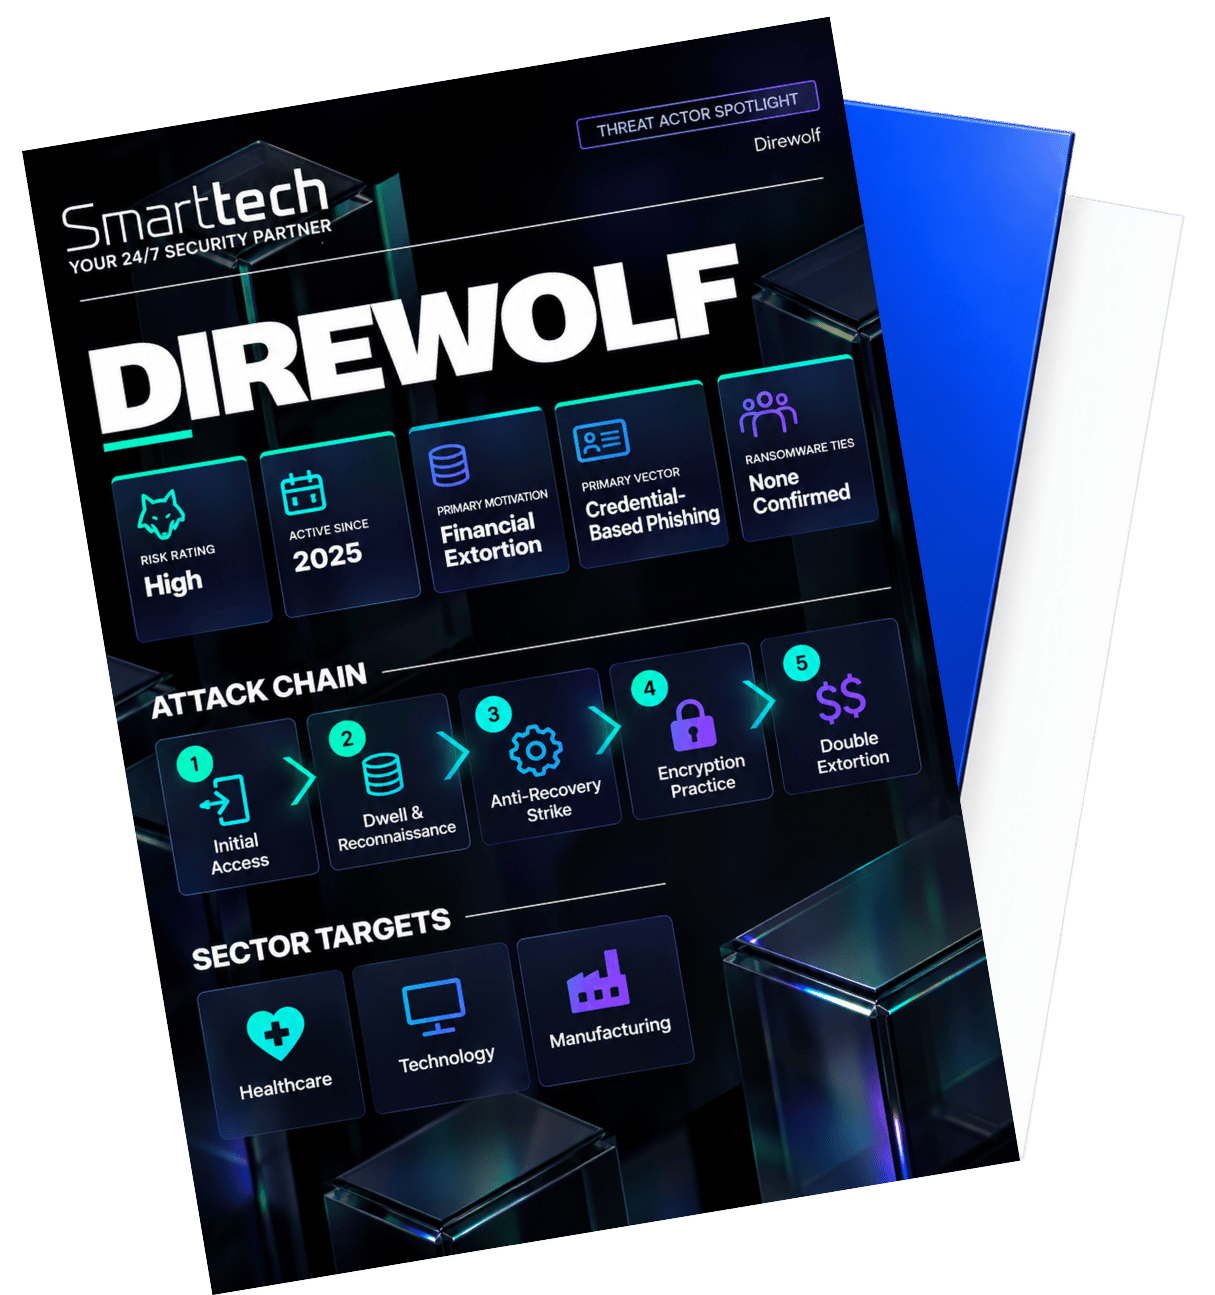
DireWolf destroys backups before encrypting. See its attack chain and how to close the window before it strikes.

Get Guide
Your recovery plan is the first thing it kills

Success here means catching the dwell-and-recon phase, not discovering the backups are already gone when you try to restore.

  • Gains entry through exposed RDP or VPN credentials, then sits quietly mapping backup infrastructure
  • Disables logging and deletes shadow copies before encryption even begins
  • Encrypts with Curve25519 and ChaCha20, then self-deletes to erase its tracks

Who This Guide is For

CISO / Head of Security

DireWolf has claimed over 100 victims across 32 countries with no confirmed ties to any established group. This guide covers the identity controls that stop credential exposure becoming an intrusion.

SOC Manager / Security Operations Lead

Days or weeks of quiet recon precede the strike. This guide explains what early-stage detection looks like before backups are targeted.

IT Director / Head of IT

Infostealer-leaked credentials are the entry point. This guide sets out the access hygiene that keeps stolen logins from becoming an active breach.