Bg Shape
Image

Fortinet and Microsoft Critical Patches, ShinyHunters Targeted Intrusion, and France’s Digital Sovereignty Shift

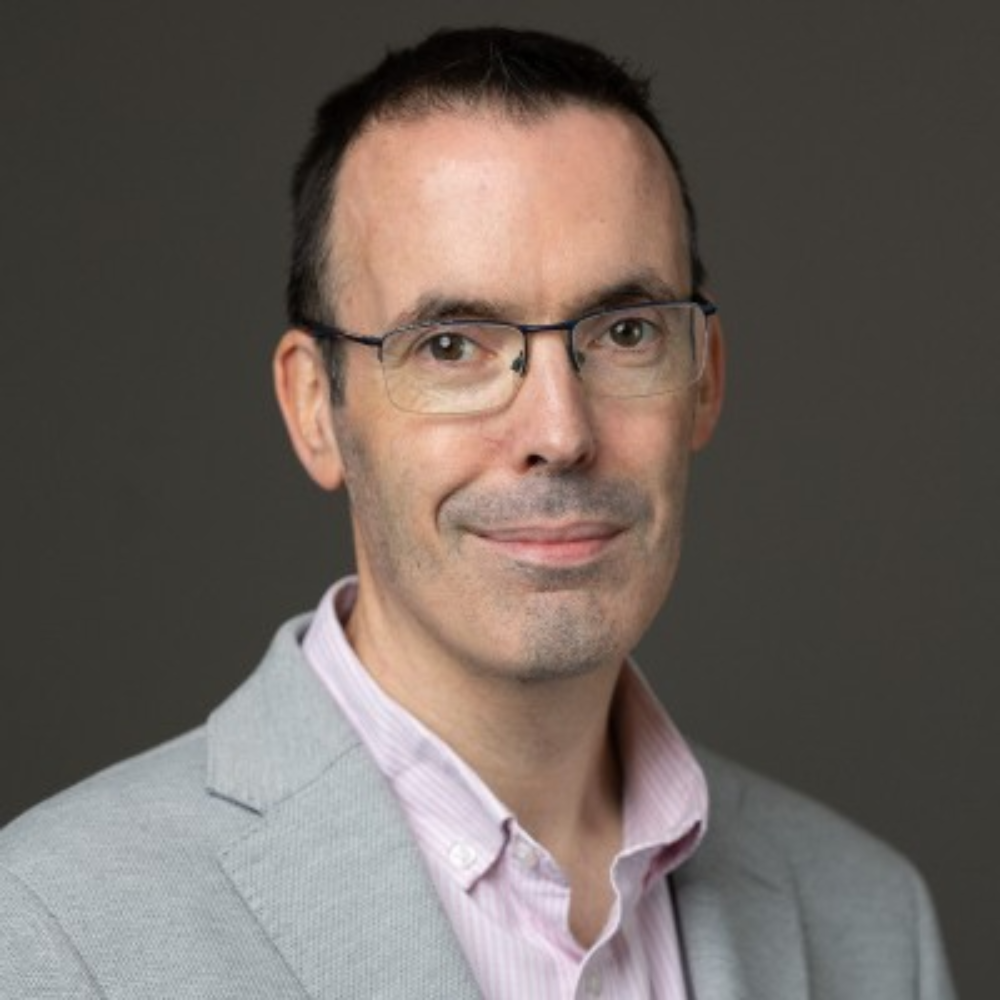
Robert Kehoe
Chief Technology Officer
Published:
January 30, 2026

This week’s Cybersecurity Week in Review highlights a number of high-severity vulnerabilities, an unusually targeted ransomware intrusion, and an interesting move by the French government around digital sovereignty and resilience.

Critical Vulnerabilities: Fortinet and Microsoft

Two patching priorities stood out this week.

Fortinet disclosed a new vulnerability affecting the FortiCloud SSO plugin used with Fortinet firewalls. With a CVSS score of 9.8, this is a critical issue, and organisations using the plugin should upgrade to the latest patch as soon as possible. Where patching cannot be applied immediately, Fortinet has provided workarounds that should be implemented without delay.

Microsoft also released an out-of-band patch for the Microsoft Office suite. This CVE scored 7.8, still firmly high severity, and should be treated as a priority update.

ShinyHunters and a Targeted Attack on Match Group

On the ransomware side, ShinyHunters claimed a number of new victims linked to Match Group, the parent company behind major dating platforms including Tinder and OkCupid.

What makes this case notable is the apparent targeting involved. The group reportedly registered the domain matchinternal.com and used it to trick a contractor into leaking credentials, enabling access into the environment.

At the time of writing, Match Group has not confirmed the full scope of the breach, but reports suggest that personal data and user tracking information may have been exposed.

France Drops US Video Conferencing Platforms

A separate development this week came from France, where the government confirmed it is dropping several US-made video conferencing tools currently in use, including Microsoft Teams, Google Meet, and Zoom.

Instead, France is deploying an internally developed platform called Visio, with an emphasis in official communications on digital sovereignty and resilience. It is a move that reflects a broader European focus on control over critical digital infrastructure.

Cyber Resilience Act Webinar

Finally, a quick note: next week I’ll be hosting a LinkedIn Live session alongside a member of our GRC team, looking at the Cyber Resilience Act and what it means for organisations preparing for compliance and operational impact.

More on that soon, and we’ll be back again next week with the next Cybersecurity Week in Review.

Read Our Latest Blogs

Blog Image
6 best MDR and XDR platforms for MSSPs in 2026

Compare six MDR and XDR platforms for MSSPs on multi-tenancy, compliance mapping and response speed, from CrowdStrike to Smarttech247 VisionX.

Blog Image
Microsoft Emergency Patch, Revolut Breach & Cisco's Second Perfect 10 CVSS

Microsoft rushes an emergency patch after last week's update broke Remote Desktop and hypervisor stability, Revolut discloses a process breach affecting 680+ high-net-worth clients, and Cisco scores another perfect 10 CVSS.
Blog Image
8 SOC Platform Requirements for 24/7 Threat Monitoring

Evaluating a threat detection and response platform? Here are the 8 requirements for 24/7 monitoring, threat intelligence, and automated response.

Bg ShapeBg Shape
BLOGS & INSIGHTS

Fortinet and Microsoft Critical Patches, ShinyHunters Targeted Intrusion, and France’s Digital Sovereignty Shift

Vulnerabilities and Exposure
Threat Actors and Campaigns
Compliance and regulations
Robert Kehoe
Chief Technology Officer
January 30, 2026

This week’s Cybersecurity Week in Review highlights a number of high-severity vulnerabilities, an unusually targeted ransomware intrusion, and an interesting move by the French government around digital sovereignty and resilience.

Critical Vulnerabilities: Fortinet and Microsoft

Two patching priorities stood out this week.

Fortinet disclosed a new vulnerability affecting the FortiCloud SSO plugin used with Fortinet firewalls. With a CVSS score of 9.8, this is a critical issue, and organisations using the plugin should upgrade to the latest patch as soon as possible. Where patching cannot be applied immediately, Fortinet has provided workarounds that should be implemented without delay.

Microsoft also released an out-of-band patch for the Microsoft Office suite. This CVE scored 7.8, still firmly high severity, and should be treated as a priority update.

ShinyHunters and a Targeted Attack on Match Group

On the ransomware side, ShinyHunters claimed a number of new victims linked to Match Group, the parent company behind major dating platforms including Tinder and OkCupid.

What makes this case notable is the apparent targeting involved. The group reportedly registered the domain matchinternal.com and used it to trick a contractor into leaking credentials, enabling access into the environment.

At the time of writing, Match Group has not confirmed the full scope of the breach, but reports suggest that personal data and user tracking information may have been exposed.

France Drops US Video Conferencing Platforms

A separate development this week came from France, where the government confirmed it is dropping several US-made video conferencing tools currently in use, including Microsoft Teams, Google Meet, and Zoom.

Instead, France is deploying an internally developed platform called Visio, with an emphasis in official communications on digital sovereignty and resilience. It is a move that reflects a broader European focus on control over critical digital infrastructure.

Cyber Resilience Act Webinar

Finally, a quick note: next week I’ll be hosting a LinkedIn Live session alongside a member of our GRC team, looking at the Cyber Resilience Act and what it means for organisations preparing for compliance and operational impact.

More on that soon, and we’ll be back again next week with the next Cybersecurity Week in Review.

Robert Kehoe

Chief Technology Officer

Robert is CTO at Smarttech247, leading engineering strategy and delivery across cybersecurity products and services. With over 15 years’ experience in software and security, and CISSP certified, he has led large-scale cloud and security initiatives, including Cloud Protection for Salesforce. Robert focuses on measurable customer outcomes and building empowered, high-performing engineering teams.

Contents:

Ready to scale your security and compliance operations?

We protect your on-premise/cloud/OT environments - 24x7x365